DNSrecon
DNSrecon is a terminal-based DNS enumeration tool that gathers detailed information about a domain via queries, brute forcing, and zone transfers. Widely used in pentesting and OSINT to discover subdomains and insecure configurations.
| Type | CLI |
| Platform | Kali / Linux |
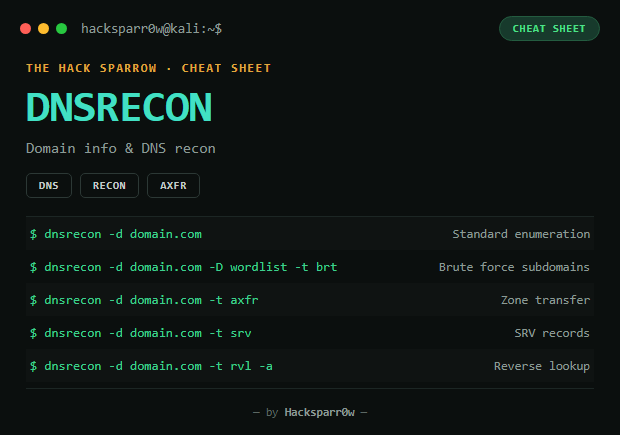
Basic commands
| Command | What it does |
|---|---|
dnsrecon -d domain.com | Standard domain enumeration (A, AAAA, MX, NS, TXT, SOA...) |
dnsrecon -d domain.com -D /usr/share/wordlists/dnsmap.txt -t brt | Subdomain brute force |
dnsrecon -d domain.com -t axfr | Zone transfer (jackpot if the DNS is misconfigured) |
dnsrecon -d domain.com -t srv | SRV record enumeration |
dnsrecon -d domain.com -t rvl -a | Reverse lookup (PTR) |
What it detects
- AXFR zone transfers (if the server is misconfigured)
- DNS wildcards
- PTR reverse zones
- SRV records
Typical result
- Discovered subdomains (www, mail, dev, api...)
- TXT records (sometimes with keys or sensitive info)
- Exposed DNS servers
- Possible AXFR (very critical)
Responsible use
These commands are for systems you own or have explicit written authorisation to test (labs, CTFs, contracted engagements). Using them against third-party infrastructure without permission is illegal in most countries.
DNSrecon es una herramienta de enumeración DNS en terminal que permite obtener información detallada sobre un dominio mediante consultas, fuerza bruta y transferencia de zonas. Muy usada en pentesting y OSINT para descubrir subdominios y configuraciones inseguras.
| Tipo | CLI |
| Plataforma | Kali / Linux |
Comandos básicos
| Comando | Qué hace |
|---|---|
dnsrecon -d dominio.com | Enumeración estándar del dominio (A, AAAA, MX, NS, TXT, SOA...) |
dnsrecon -d dominio.com -D /usr/share/wordlists/dnsmap.txt -t brt | Fuerza bruta de subdominios |
dnsrecon -d dominio.com -t axfr | Transferencia de zona (jackpot si el DNS está mal configurado) |
dnsrecon -d dominio.com -t srv | Enumeración de registros SRV |
dnsrecon -d dominio.com -t rvl -a | Reverse lookup (PTR) |
Qué detecta
- Transferencias de zona AXFR (si el servidor está mal configurado)
- Wildcard DNS
- Zonas reversas PTR
- Registros SRV
Resultado típico
- Subdominios descubiertos (www, mail, dev, api...)
- Registros TXT (a veces con claves o información sensible)
- Servidores DNS expuestos
- Posible AXFR (muy crítico)
Uso responsable
Estos comandos son para entornos propios o con autorización explícita por escrito (laboratorios, CTF, auditorías contratadas). Usarlos contra infraestructura ajena sin permiso es ilegal en la mayoría de países.