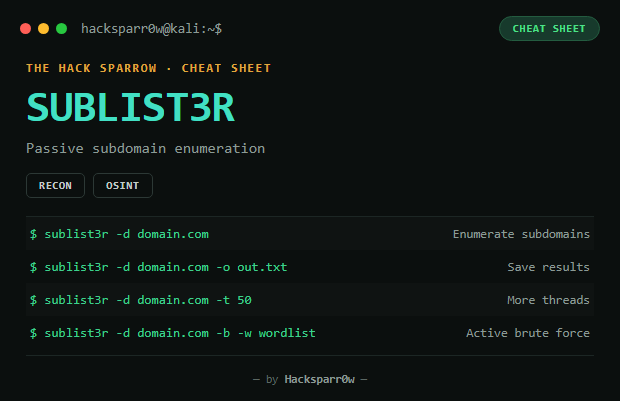
Sublist3r is a passive OSINT tool for enumerating subdomains using multiple search engines and external services. Fast, lightweight, and heavily used in the initial recon phase.
Notes: combine it with Amass and Subfinder for maximum coverage. After getting subdomains, run Nmap against them; to know which are alive, pair it with httprobe/httpx.
Responsible use
These commands are for systems you own or have explicit written authorisation to test (labs, CTFs, contracted engagements). Using them against third-party infrastructure without permission is illegal in most countries.
Sublist3r es una herramienta de OSINT pasivo para enumerar subdominios usando múltiples motores de búsqueda y servicios externos. Rápida, ligera y muy usada en la fase inicial de reconocimiento.
Depende de información pública, puede devolver entradas antiguas
Muchas fuentes compatibles
No detecta servicios ni puertos
Notas: combínalo con Amass y Subfinder para máxima cobertura. Tras obtener los subdominios, lánzale Nmap; si quieres saber cuáles están vivos, combina con httprobe/httpx.
Uso responsable
Estos comandos son para entornos propios o con autorización explícita por escrito (laboratorios, CTF, auditorías contratadas). Usarlos contra infraestructura ajena sin permiso es ilegal en la mayoría de países.