Burp Suite
Burp Suite is the single most important tool for web pentesting. It lets you intercept, modify and analyse traffic between the browser and the server. In web pentesting it's the industry standard.
It's used to intercept HTTP/HTTPS requests, manipulate parameters, explore APIs, find vulnerabilities (XSS, SQLi, RCE, LFI...), automate scans, and run repeated attacks with Intruder/Repeater/Turbo Intruder.
| Install | burpsuite (bundled in Kali) · Pro via the official .jar |
| Browser proxy | 127.0.0.1:8080 |
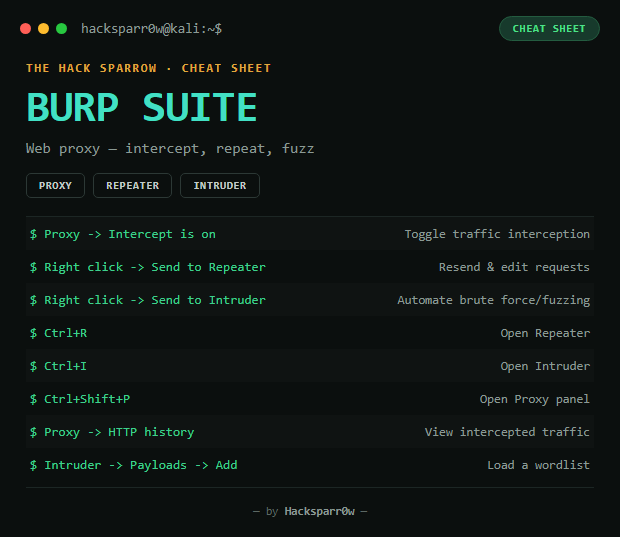
Getting started
- Open Burp Suite
- Go to Proxy → Intercept
- Set the browser's proxy to
127.0.0.1:8080 - Burp will start intercepting traffic
1. Proxy (Intercept)
Intercepts HTTP/HTTPS requests and lets you modify parameters on the fly: toggle intercept, view headers, change cookies, change form values.
Proxy → Intercept → Intercept is on2. Repeater — manual attacks
Lets you resend a request many times while tweaking parameters. Typical use: testing XSS, testing SQL injection, manual fuzzing, modifying tokens and cookies.
Right-click → Send to Repeater3. Intruder — brute force / fuzzing
Automation for login brute-forcing, directory discovery, parameter fuzzing, and wordlist-based attacks (SecLists).
Right-click → Send to Intruder
Intruder → Payloads → Add → /usr/share/wordlists/seclists
4-7. Scanner, Decoder, Comparer, Logger
| Module | Function |
|---|---|
| Scanner (Pro only) | Automated scanning for SQLi, XSS, path traversal, CSRF, LFI/RFI, open redirects, insecure cookies |
| Decoder | Encodes/decodes Base64, URL encode, Hex, HTML entity |
| Comparer | Compares two responses: valid vs invalid, vulnerable vs non-vulnerable |
| Logger | Full log of every request Burp has seen |
Quick commands and actions
| Action | How |
|---|---|
| Intercept traffic | Proxy → Intercept is on |
| Send to Repeater | Right click → Send to Repeater |
| Send to Intruder | Right click → Send to Intruder |
| View parameters/history | Proxy → HTTP history |
| Load a wordlist in Intruder | Payloads → Add → /usr/share/wordlists/seclists |
Useful shortcuts
| Shortcut | Action |
|---|---|
| Ctrl + I | Send to Intruder |
| Ctrl + R | Send to Repeater |
| Ctrl + Shift + P | Open the Proxy panel |
| Ctrl + Shift + R | Open Repeater |
| Ctrl + Shift + I | Open Intruder |
Responsible use
These commands are for systems you own or have explicit written authorisation to test (labs, CTFs, contracted engagements). Using them against third-party infrastructure without permission is illegal in most countries.
Burp Suite es la herramienta más importante para pentesting web. Permite interceptar, modificar y analizar el tráfico entre el navegador y el servidor. En pentesting web es el estándar de la industria.
Se usa para interceptar peticiones HTTP/HTTPS, manipular parámetros, explorar APIs, encontrar vulnerabilidades (XSS, SQLi, RCE, LFI...), automatizar escaneos, y lanzar ataques repetitivos con Intruder/Repeater/Turbo Intruder.
| Instalación | burpsuite (viene en Kali) · Pro con el .jar oficial |
| Proxy del navegador | 127.0.0.1:8080 |
Primeros pasos
- Abre Burp Suite
- Ve a Proxy → Intercept
- Configura el proxy del navegador en
127.0.0.1:8080 - Burp empezará a interceptar tráfico
1. Proxy (Intercept)
Intercepta las peticiones HTTP/HTTPS y permite modificar parámetros al vuelo: encender/apagar intercept, ver cabeceras, cambiar cookies, cambiar valores de formularios.
Proxy → Intercept → Intercept is on2. Repeater — ataques manuales
Permite reenviar una petición muchas veces modificando parámetros. Uso típico: probar XSS, probar SQL injection, fuzzing manual, modificar tokens y cookies.
Right-click → Send to Repeater3. Intruder — fuerza bruta / fuzzing
Automatización de fuerza bruta de logins, descubrimiento de directorios, fuzzer de parámetros, y ataques con wordlists (SecLists).
Right-click → Send to Intruder
Intruder → Payloads → Add → /usr/share/wordlists/seclists
4-7. Scanner, Decoder, Comparer, Logger
| Módulo | Función |
|---|---|
| Scanner (solo Pro) | Escaneo automático de SQLi, XSS, path traversal, CSRF, LFI/RFI, open redirects, cookies inseguras |
| Decoder | Codifica/decodifica Base64, URL encode, Hex, HTML entity |
| Comparer | Compara dos respuestas: válida vs inválida, vulnerable vs no vulnerable |
| Logger | Registro completo de todo el tráfico visto por Burp |
Comandos y acciones rápidas
| Acción | Cómo |
|---|---|
| Interceptar tráfico | Proxy → Intercept is on |
| Enviar a Repeater | Right click → Send to Repeater |
| Enviar a Intruder | Right click → Send to Intruder |
| Ver parámetros/historial | Proxy → HTTP history |
| Cargar wordlist en Intruder | Payloads → Add → /usr/share/wordlists/seclists |
Atajos útiles
| Atajo | Acción |
|---|---|
| Ctrl + I | Enviar a Intruder |
| Ctrl + R | Enviar a Repeater |
| Ctrl + Shift + P | Abrir panel de Proxy |
| Ctrl + Shift + R | Abrir Repeater |
| Ctrl + Shift + I | Abrir Intruder |
Uso responsable
Estos comandos son para entornos propios o con autorización explícita por escrito (laboratorios, CTF, auditorías contratadas). Usarlos contra infraestructura ajena sin permiso es ilegal en la mayoría de países.